 Esecurityplanet
N0va Phishkit Exploits Microsoft Logins Across North America and Europe
Article Content

- •N0va phishkit targets Microsoft logins, bypassing MFA.
- •Affected sectors include government, healthcare, and technology.
- •Security teams should enhance monitoring and restrict device-code authentication.
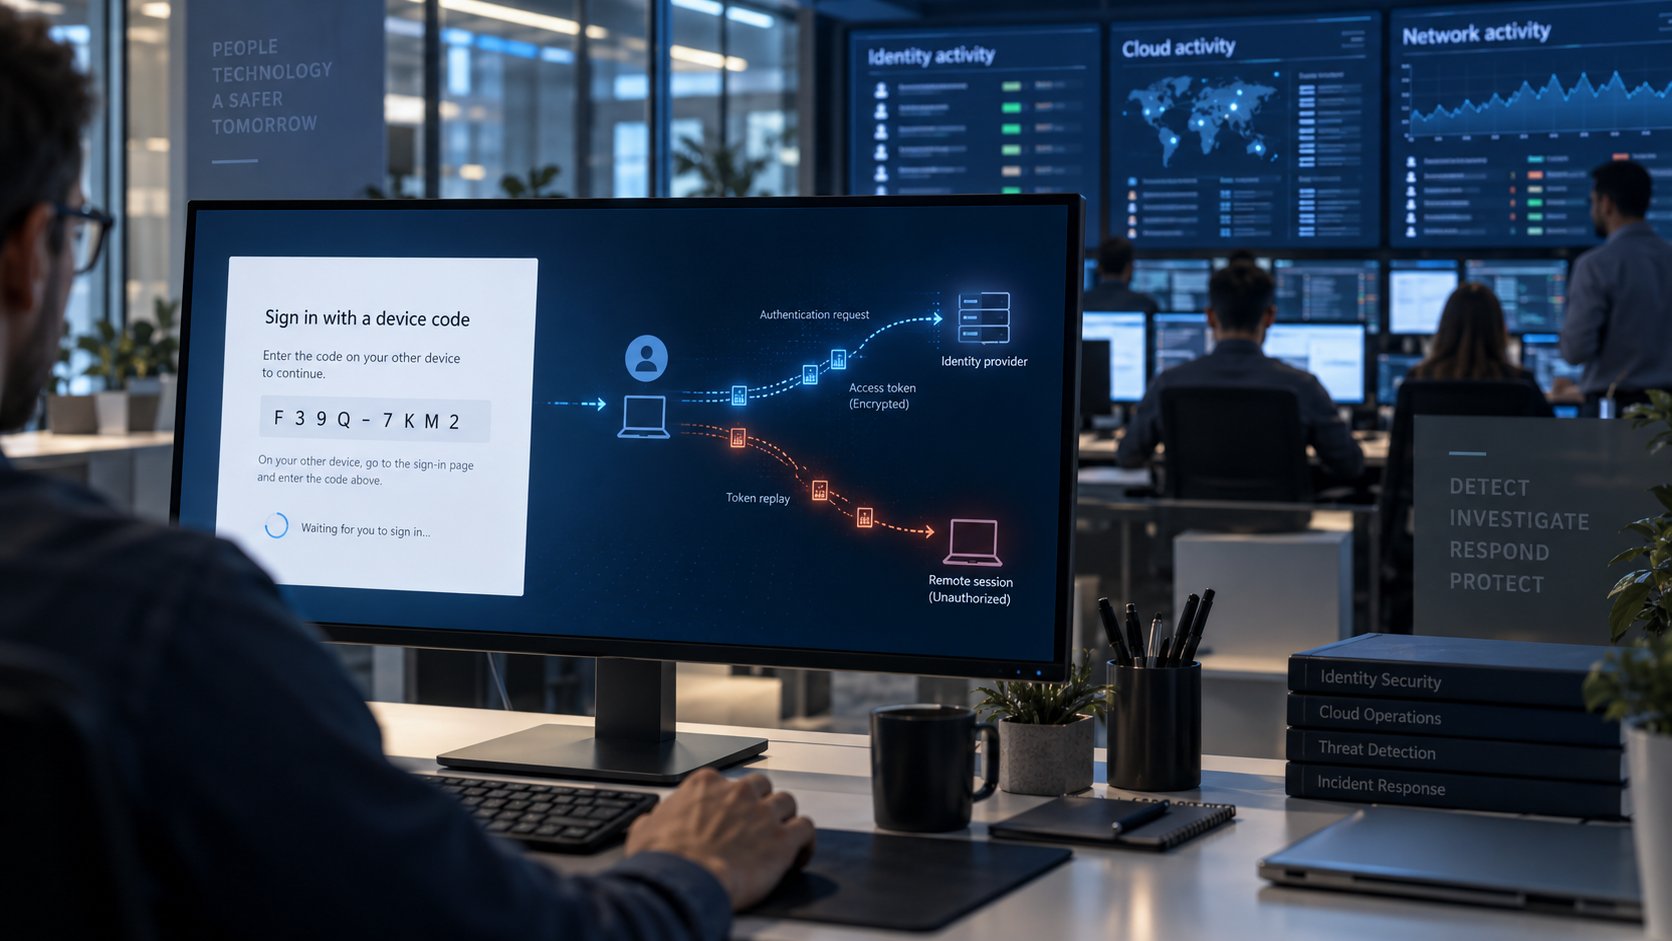
The N0va phishkit has been identified as a significant threat targeting organizations in North America and Europe, including government, technology, consulting, and healthcare sectors. It exploits Microsoft device-code authentication to obtain access and refresh tokens, even after users complete multifactor authentication (MFA). The attack method involves lures impersonating trusted brands and leveraging compromised websites and cloud infrastructure. ANY.RUN disclosed the campaign in September 2026, highlighting the need for enhanced identity monitoring and access controls. Microsoft previously documented similar vulnerabilities in April 2026, indicating a recurring issue. Security teams are advised to audit device-code authentication and monitor for suspicious activity to mitigate risks. The scope of the attack is extensive, affecting enterprises managing Microsoft identities across multiple jurisdictions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Microsoft in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…