 science.nasa.gov
NASA's Swift Observatory Rescue Mission Advances with Successful Testing
Article Content

- •Katalyst's LINK spacecraft completed critical environmental tests at NASA Goddard.
- •The Swift Observatory's orbit is decaying rapidly, necessitating immediate action.
- •The launch of the LINK spacecraft is scheduled for June 2026 to save Swift.
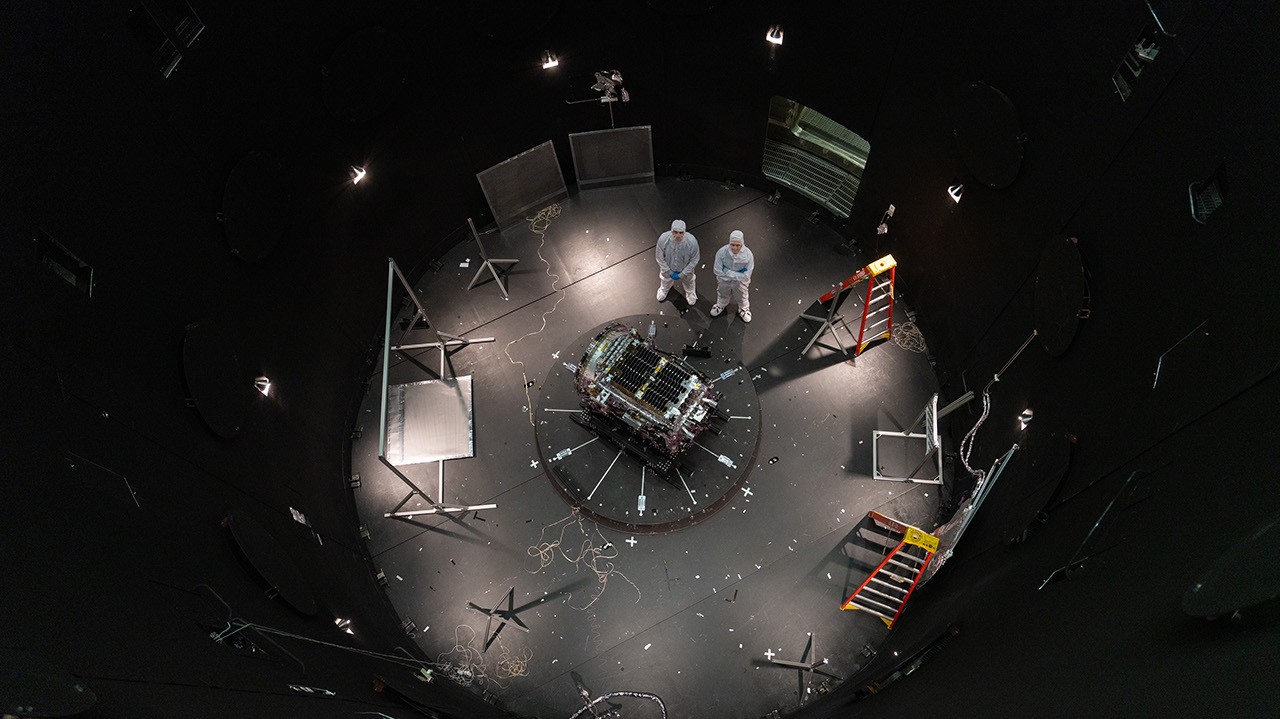
NASA's Neil Gehrels Swift Observatory is at risk of re-entering the atmosphere due to a decaying orbit. Katalyst Space Technologies has completed environmental tests of its LINK robotic spacecraft at NASA's Goddard Space Flight Center, crucial for the upcoming mission to boost Swift's orbit. The mission was initiated after Swift's orbit began to decline faster than expected, prompting NASA to contract Katalyst in September 2025. The LINK spacecraft has undergone vibration and thermal-vacuum testing, simulating launch conditions and space environments. The launch is scheduled for June 2026, with integration into a Northrop Grumman Pegasus rocket planned for early June. Swift's mission director emphasized the urgency of the situation, stating that without intervention, the observatory could re-enter the atmosphere later this year.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…