 www.theguardian.com
Nathan Gill Sentenced for Bribery Linked to Pro-Russian Influence
Article Content

- •Nathan Gill was sentenced to 10.5 years for accepting bribes to promote pro-Russian statements.
- •He received at least £30,000 from Oleg Voloshyn, an alleged Russian asset, during his tenure as an MEP.
- •The UK government is reviewing foreign financial influence in politics following Gill's conviction.
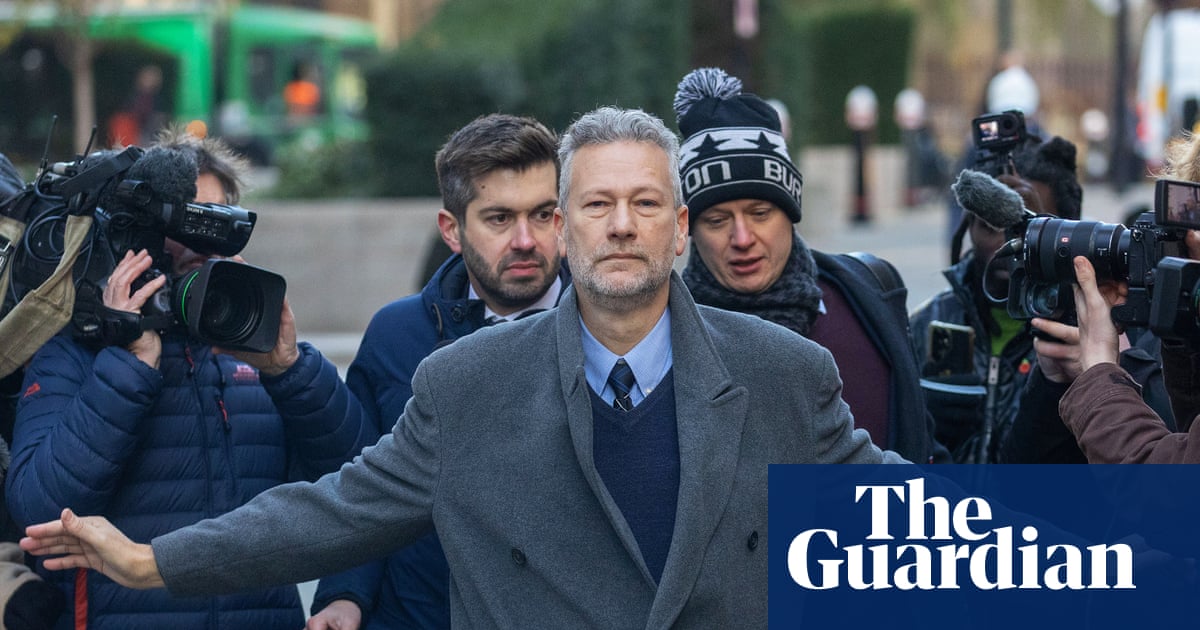
Nathan Gill, former leader of Reform UK in Wales, was sentenced to ten and a half years in prison for accepting bribes to promote pro-Russian narratives while serving as a Member of the European Parliament. He received at least £30,000 from Oleg Voloshyn, an alleged Russian asset, to make statements beneficial to the Kremlin regarding Ukraine. Gill pleaded guilty to eight counts of bribery, which occurred between December 2018 and July 2019. His actions were seen as a significant betrayal of public trust, as he advanced narratives advantageous to Russian interests during a critical period before the full-scale invasion of Ukraine. The UK government has initiated the Rycroft Review to address foreign financial influence in politics, following Gill's conviction. The case raises questions about the intersection of corruption and foreign interference in democratic processes. Investigations into Gill's connections and the broader implications for Reform UK are ongoing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…