 Aa.Tr
NATO Commander Unveils Strategy to Deter Russian Aggression
Article Content

- •NATO's new strategy includes blocking, blunting, and breaking enemy forces.
- •General Grynkewich emphasized NATO's defensive posture and readiness to deter aggression.
- •The strategy involves multi-domain operations across land, air, sea, space, and cyber.
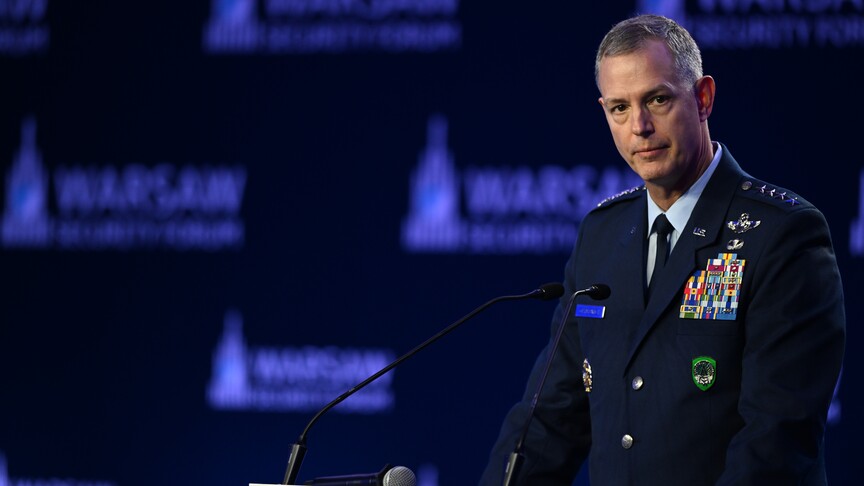
On October 12, 2026, NATO's Supreme Allied Commander Europe, General Alexus Grynkewich, presented a three-stage military strategy at the Warsaw Security Forum aimed at countering potential Russian attacks. The strategy, termed 'block, blunt, and break,' emphasizes blocking initial assaults, blunting ongoing offensives, and breaking enemy forces if necessary. Grynkewich reassured that NATO does not view conflict as imminent but is prepared to deter aggression and maintain peace. The strategy incorporates multi-domain operations utilizing land, air, sea, space, and cyber capabilities. NATO's focus is on preventing adversaries from seizing and holding territory rather than inflicting strategic defeats. The alliance is enhancing operational readiness through exercises and investments in advanced military capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is the 'block, blunt, and break' strategy?
Is NATO preparing for imminent conflict?
How is NATO enhancing its military capabilities?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…