 Rusi
NATO's Need for Integrated Cyber Deterrence Against China
Article Content
Browse articles 
- •NATO must adopt a whole-of-government approach to cyber threats.
- •China's cyber operations are part of a broader strategy, not isolated incidents.
- •Effective deterrence strategies are critical to countering state-sponsored cyber espionage.
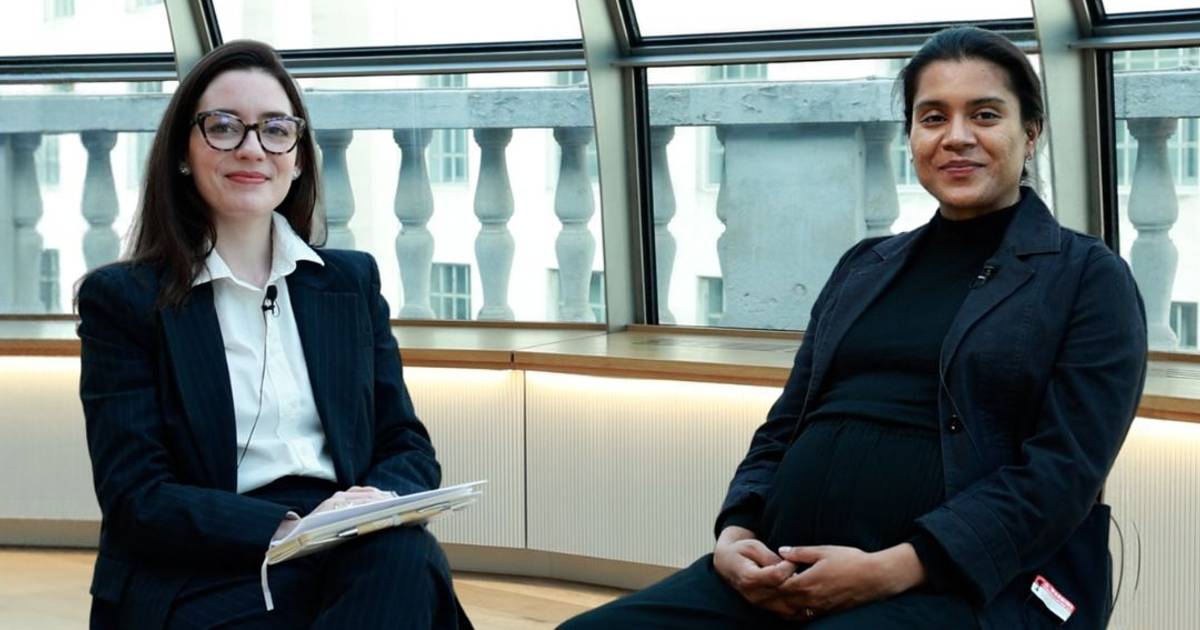
NATO member states are urged to adopt a whole-of-government approach to counter China's cyber espionage tactics, as highlighted by Dr. Louise Marie Hurel and Dr. Gareth Mott. They emphasize that cyber activities should not be treated in isolation but integrated with broader statecraft. The commentary discusses how China has utilized cyber operations as a means to test escalation strategies, often misperceived by the West as isolated incidents. The experts stress the importance of developing effective deterrence strategies to impose costs on adversaries. Current strategies are deemed insufficient to address the coordinated nature of these state-sponsored cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
More articles in this cluster (2)
Common questions
What is NATO's current approach to cyber threats?
NATO's current approach is criticized for treating cyber threats in isolation rather than integrating them with broader statecraft.
How is China using cyber operations strategically?
China employs cyber operations as a testing ground for escalation, often misinterpreted by the West as isolated incidents.
What do experts recommend for NATO's response?
Experts recommend a whole-of-government approach to impose costs on adversaries effectively.
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…