 Journalismpakistan
NCCIA Summons Columnist Over PAS Complaint on Corruption Remarks
Article Content

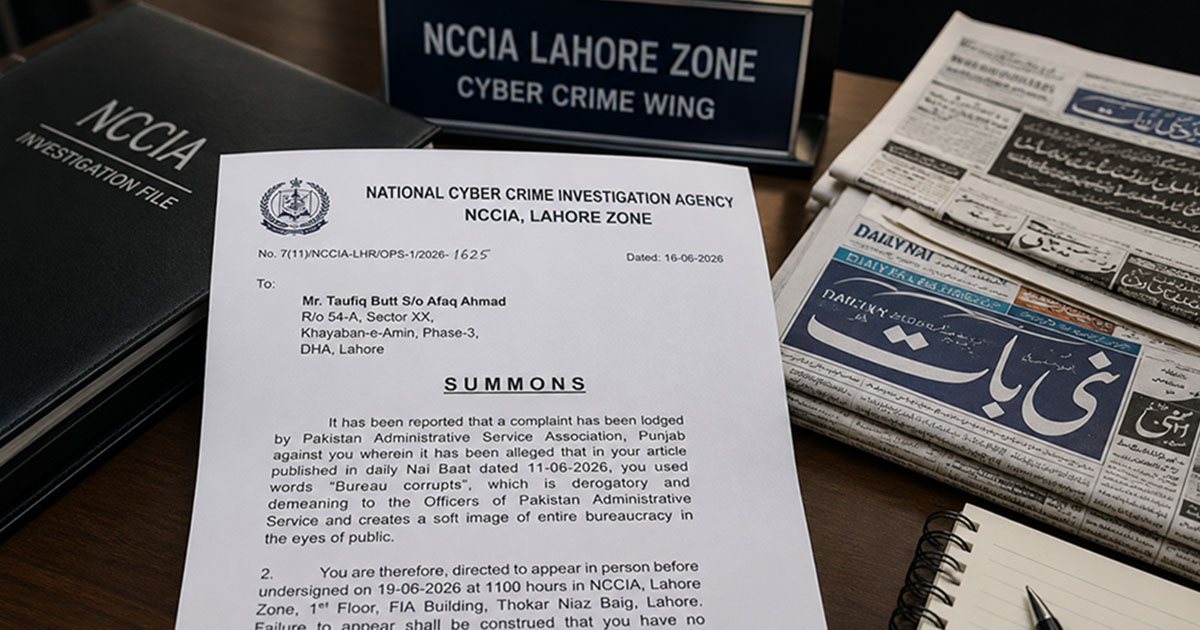
- •Taufiq Butt is summoned by the NCCIA over a complaint regarding his column's language.
- •The PAS Association claims the phrase 'Bureau corrupts' damages the reputation of civil servants.
- •The case raises concerns about the intersection of cybercrime laws and freedom of expression.
The National Cyber Crime Investigation Agency (NCCIA) has summoned columnist Taufiq Butt to respond to a complaint from the Pakistan Administrative Service (PAS) Association regarding derogatory language in his column. The PAS Association claims Butt's use of the phrase 'Bureau corrupts' in his June 11 article unfairly maligns civil servants and damages their reputation. The NCCIA's notice requires Butt to appear in Lahore on June 19 to present his defense. This case highlights ongoing tensions between freedom of expression and reputation protection in Pakistan's media landscape, especially in light of recent amendments to the Prevention of Electronic Crimes Act (PECA). The situation is drawing attention from media stakeholders and could influence future discussions on the boundaries of journalistic commentary. The NCCIA's involvement reflects the increasing scrutiny of cybercrime laws in relation to media expression.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…