
OnionDrop Loader Campaign Delivers LegionLoader and Infostealers at Scale
Article Content

- •OnionDrop loader is delivering LegionLoader and multiple infostealers.
- •Over 645 unique DLL samples linked to OnionDrop were identified in recent months.
- •The campaign utilizes DLL sideloading techniques to evade detection.
A new loader campaign, OnionDrop, is actively delivering malicious payloads, including LegionLoader and multiple infostealers, to a wide range of victims. Researchers identified over 645 unique DLL samples associated with OnionDrop between February 28 and May 20, 2026. The campaign employs sophisticated DLL sideloading techniques to evade detection and has been operational since at least early 2026. Current deliveries remain active, indicating a significant ongoing threat to various systems. The scale of the operation and its advanced evasion methods raise serious concerns within the cybersecurity community.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track LegionLoader in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Active Exploitation of Siemens Software Center Vulnerability in ClickFix Campaign Siemens has confirmed that a DLL side-loading vulnerability (CVE-2026-110936) in Siemens Software Center is actively being exploited in malware attacks. The vulnerability allows attackers to execute malicious code by placing a specially crafted DLL in a directory searched by the application. Siemens first disclosed…
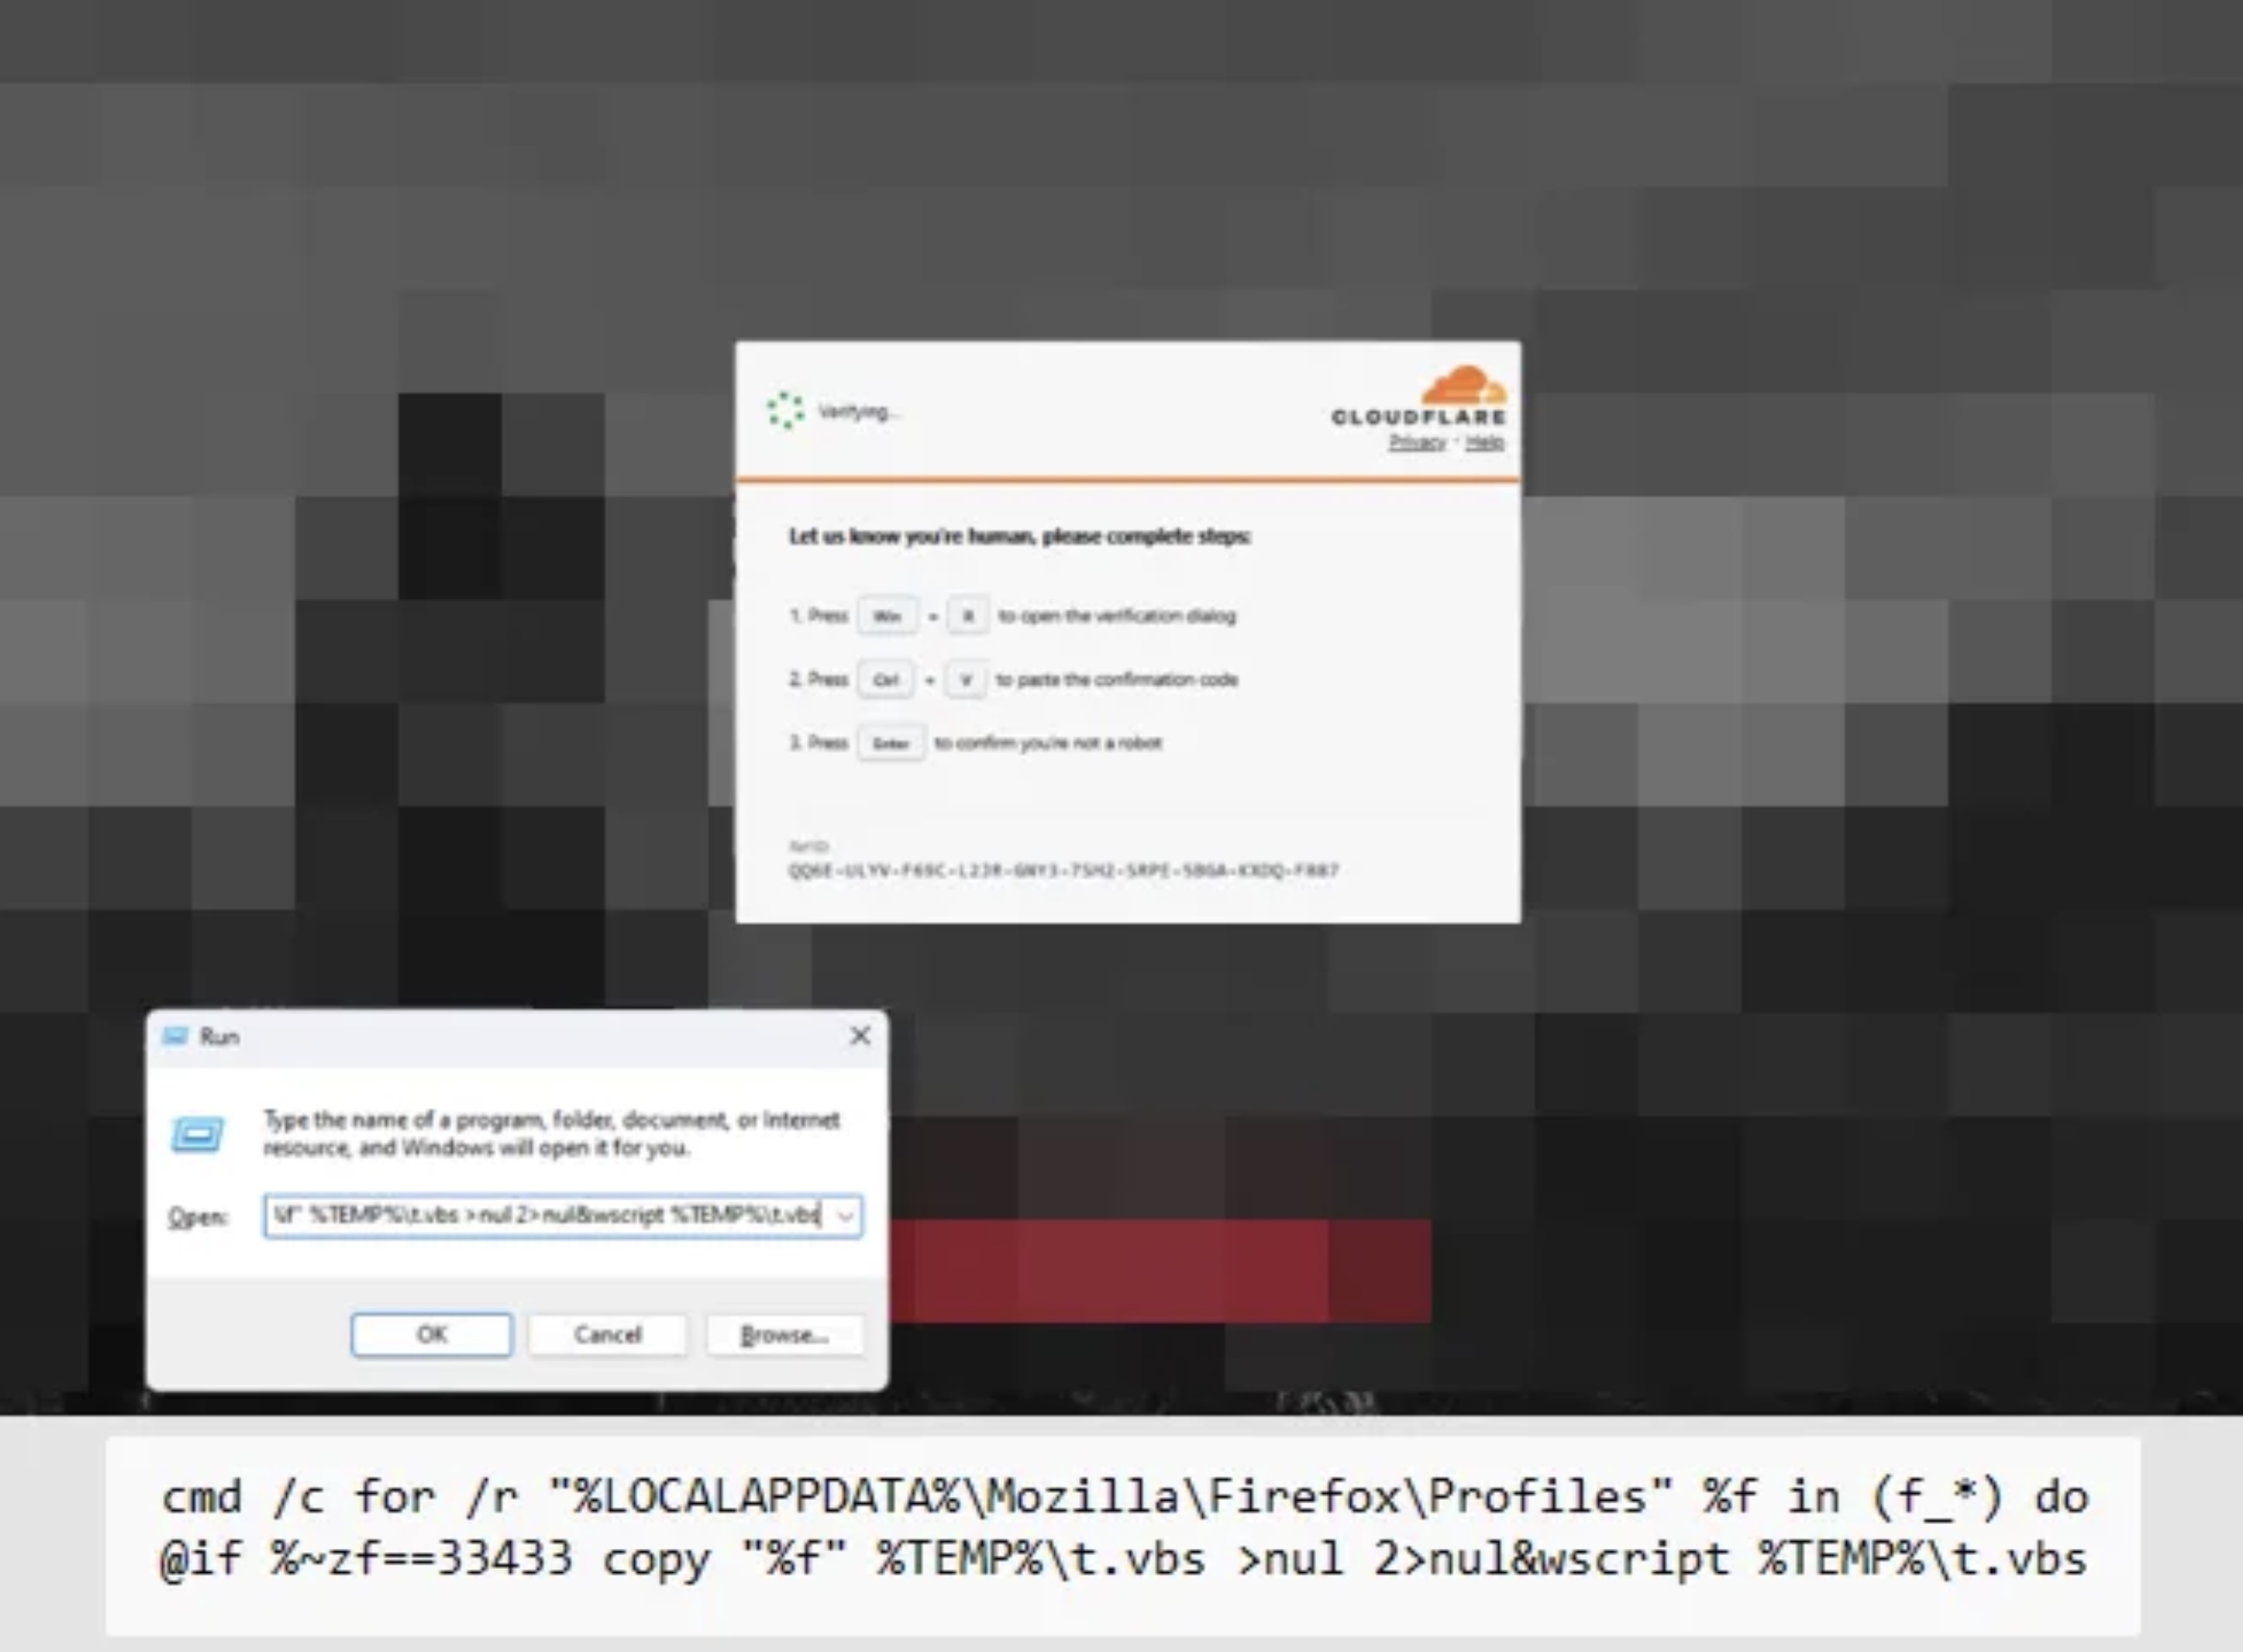 ClickFix Malware Technique Expands with ROMULUS Server Cybercriminals are increasingly utilizing the ClickFix social engineering technique to deploy malware, as evidenced by the discovery of the ROMULUS server, which can deliver multiple payloads. ClickFix tricks users into executing malicious commands on their own machines, effectively bypassing traditional security…