 journals.aps.org
New Technique Reduces Qubit Leakage by 98.4%, Enhancing Quantum Error Correction
Article Content

- •QuTech achieved a 98.4% reduction in qubit leakage during measurement.
- •The leakage reduction unit operates without adding time to the measurement process.
- •The LRU maintains a fidelity of 99.2% while suppressing logical error rates.
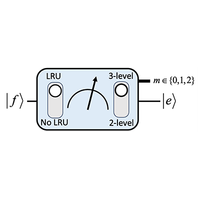
Researchers at QuTech, Delft University of Technology, have developed a leakage reduction unit (LRU) that achieves a 98.4% reduction in qubit leakage during measurement, significantly improving quantum error correction (QEC) processes. This leakage, which occurs when quantum information escapes the computational state, introduces errors that complicate QEC with superconducting qubits. The LRU operates concurrently with transmon measurement and utilizes a protocol adapted from double-drive reset of population (DDROP), maintaining a high fidelity of 99.2% in assigning computational states. The integration of LRU with neural-network decoding has successfully suppressed logical error rates in both memory and stability QEC experiments without post-selection. This advancement is a crucial step toward building more reliable and scalable quantum computers, addressing a fundamental source of error at its origin. The findings promise to enhance the stability and scalability of future quantum systems.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is the significance of the 98.4% leakage reduction?
How does the LRU improve measurement processes?
What are the implications for future quantum computing?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…