 Devdiscourse
New Zealand Targets Russian Cyber Actors and Sanctions Evasion Networks
Article Content

- •New Zealand imposed sanctions on 20 individuals and entities linked to Russian cyber operations.
- •The sanctions include targeting an alternative payment provider used for sanctions evasion.
- •This marks New Zealand's 35th round of sanctions since the Russia Sanctions Act was enacted.
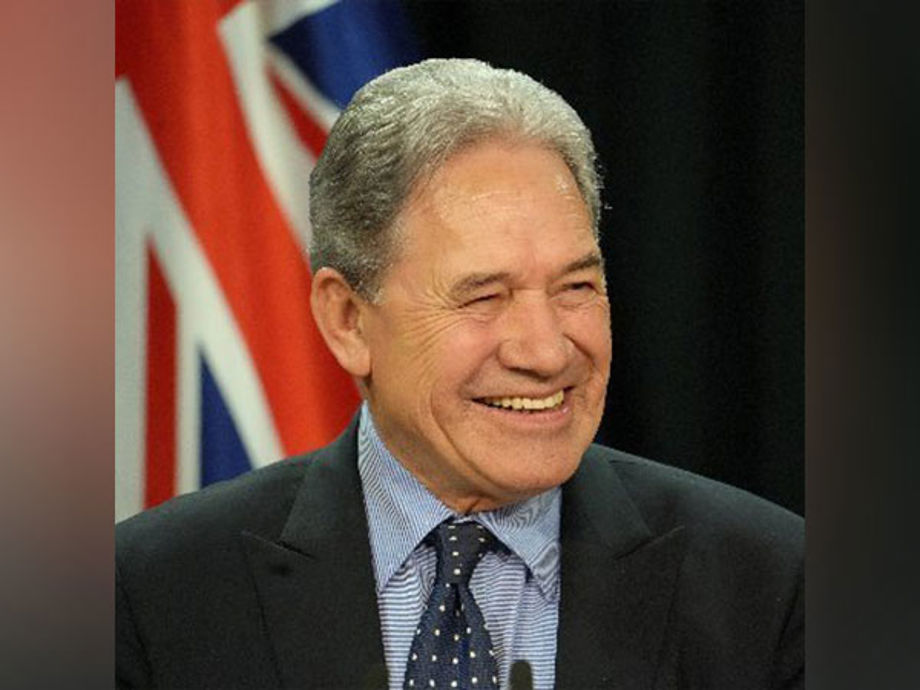
On May 7, 2026, New Zealand announced its 35th round of sanctions against Russia, focusing on cyber actors and sanctions evasion networks supporting the war against Ukraine. Foreign Minister Winston Peters designated 20 individuals and entities linked to Russian cybercrime, propaganda, and military support. The sanctions also target an alternative payment provider allegedly facilitating sanctions evasion. This move aligns with international efforts to disrupt financial channels aiding Russia's military campaign. Since the Russia Sanctions Act's enactment in March 2022, New Zealand has sanctioned over 2,000 individuals and entities. The announcement reflects a growing concern over the role of cyber operations and disinformation in geopolitical conflicts. Peters emphasized that those misusing online platforms will face consequences, highlighting the need for robust measures against hybrid warfare tactics.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…