 Guardian.Ng
NgCERT Warns of $2 Million ATM Cash-Out Cyberattack on UBA Senegal
Article Content

- •NgCERT reported a $2 million loss from ATM cash-out attacks on UBA Senegal.
- •Attackers compromised card authorization systems, enabling large-scale fraudulent withdrawals.
- •Financial institutions are urged to enhance security measures to prevent future attacks.
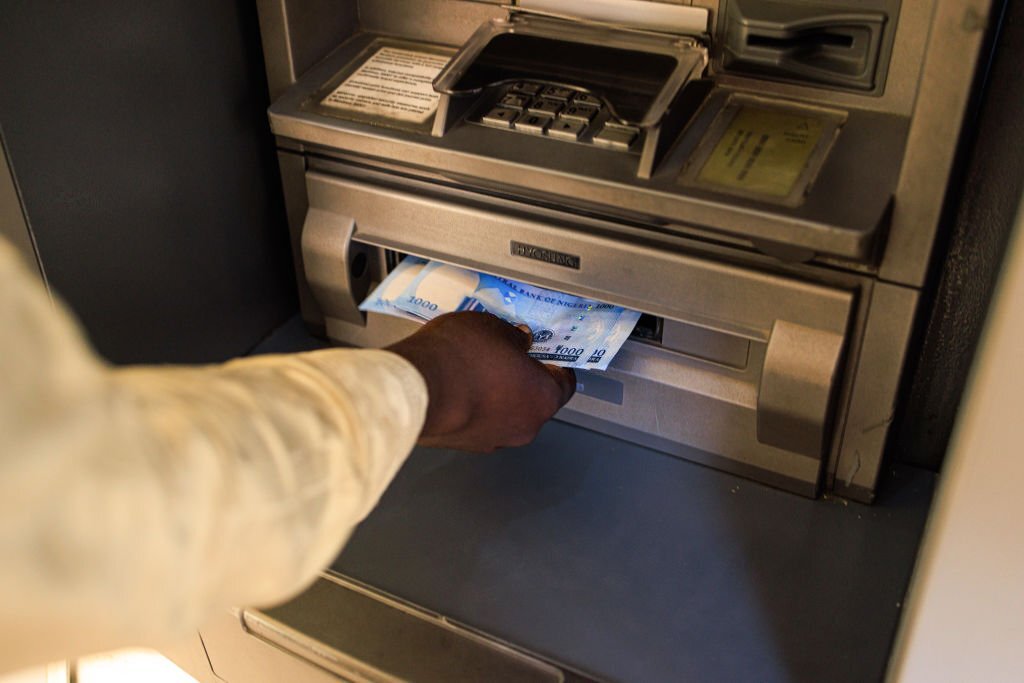
NgCERT issued a cybersecurity advisory on June 25, 2026, alerting financial institutions of a coordinated ATM cash-out attack that resulted in losses exceeding $2 million at UBA Senegal. The attack involved 3,421 fraudulent withdrawals executed by cybercriminals who compromised the bank's card authorization infrastructure. Attackers gained access through phishing, supply chain vulnerabilities, or insider assistance, allowing them to manipulate transaction controls. This incident highlights a sophisticated methodology that poses a significant threat to banks across Africa. NgCERT emphasized the potential for massive financial losses, operational disruptions, and reputational damage if such vulnerabilities are exploited. Recommendations include strengthening security controls, implementing multi-factor authentication, and enhancing real-time transaction monitoring. The advisory underscores the urgency for banks to act to prevent similar incidents.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Ploutus and UBA Senegal in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 U.S. Sanctions Target Tren de Aragua's ATM Jackpotting Scheme On September 30, 2026, the U.S. Treasury's OFAC sanctioned 10 individuals linked to Tren de Aragua (TdA), a Foreign Terrorist Organization, for their involvement in an ATM jackpotting scheme that stole over $40 million from U.S. banks. The scheme utilized malware to force ATMs to dispense cash without debiting…
 Citrix NetScaler Critical Vulnerabilities Exploited: Urgent Patching Required Citrix NetScaler ADC and Gateway products are affected by critical vulnerabilities CVE-2026-88771 and CVE-2026-88772, both assigned a CVSS score of 9.5. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on September 27, 2026, and mandated…