 Techradar
Norwegian Military's Use of Chinese Rental Cars Raises Security Concerns
Article Content

- •Chinese rental cars used by Norwegian military recorded sensitive footage during exercises.
- •Dashcams captured soldiers typing security codes, raising operational security concerns.
- •Experts caution against framing the incident as deliberate espionage without further evidence.
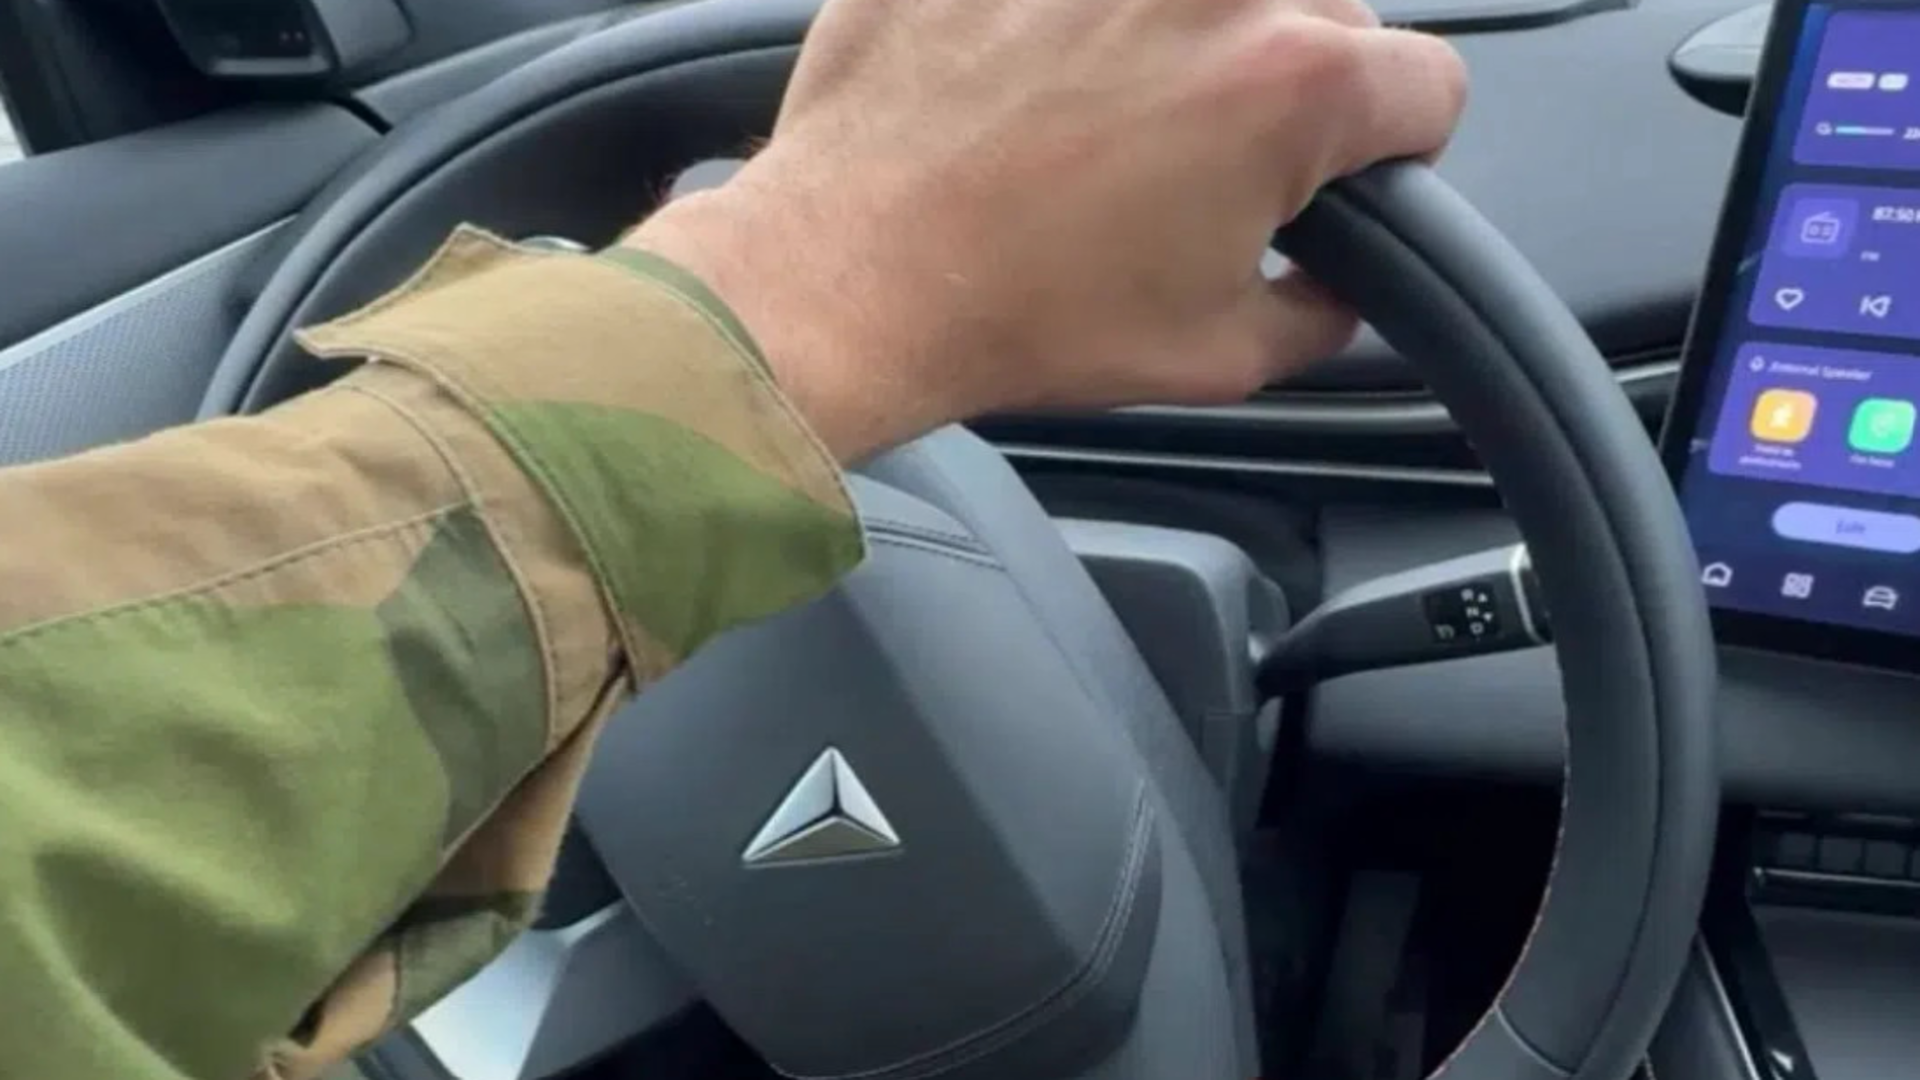
Norwegian forces used Chinese-made rental cars during a military exercise, which recorded sensitive footage of soldiers and security codes. The cars, rented from Hertz Norway, contained dashcams that captured soldiers entering and exiting the vehicles, as well as typing gate codes. Although the footage was deleted by soldiers after discovery, the incident has raised significant concerns about data security and operational security within the Norwegian Armed Forces. Experts indicate that while the risks are real, they do not necessarily indicate deliberate espionage by China. The incident highlights vulnerabilities in military practices and the implications of using connected civilian technologies. The exact extent of data access and whether it was transmitted outside the vehicles remains unclear.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track First Rent A Car Norway AS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific data was recorded?
How did the military respond to the recordings?
Is there evidence of espionage?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…