 Therecord.Media
NSA Restructures into Five Mission Centers Focusing on Cybersecurity and AI
Article Content

- •NSA is restructuring into five new mission centers to enhance operational efficiency.
- •Focus areas include cybersecurity, AI, China, combat support, and global intelligence.
- •Full operational capability for the new centers is expected by January 2027.
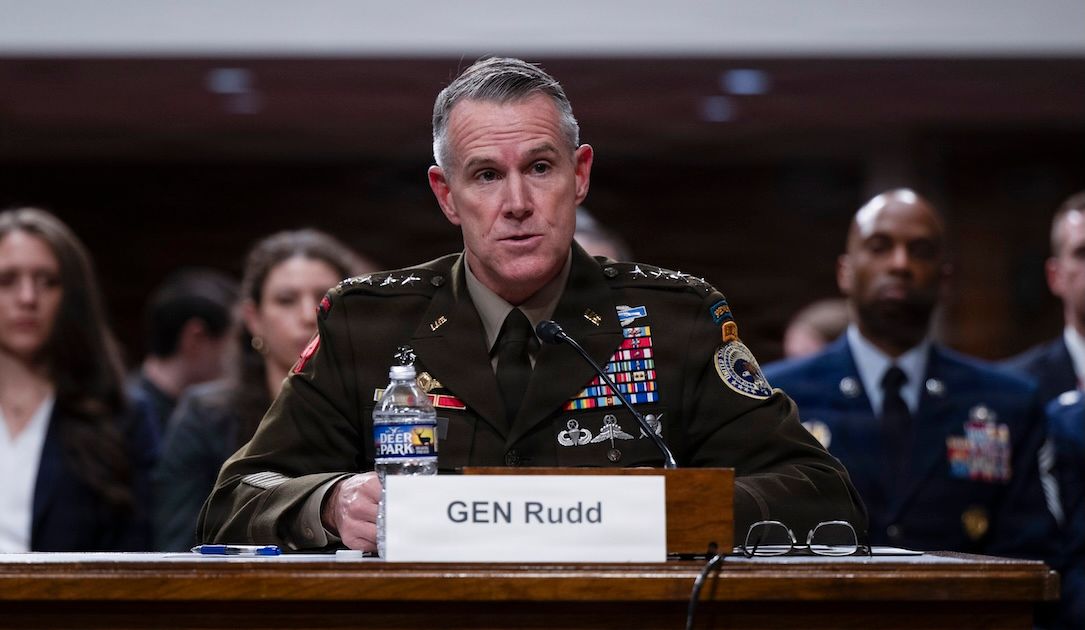
The National Security Agency (NSA) is undergoing a significant reorganization to create five new mission centers focused on artificial intelligence, cybersecurity, China, combat support, and global intelligence. This restructuring aims to enhance the agency's ability to respond to evolving threats and improve operational efficiency. The changes were announced by Army Gen. Joshua Rudd, who leads both the NSA and U.S. Cyber Command. The NSA's previous major reorganization, known as NSA21, occurred around a decade ago and aimed to consolidate its cyber operations. The new mission centers are expected to achieve full operational capability by January 2027. The revival of the elite hacking group Tailored Access Operations is also part of this shift, although its exact placement within the new structure remains unclear. The NSA's focus on China and AI reflects growing concerns over Beijing's cyber capabilities and the need to protect U.S. technologies from industrial-scale extraction efforts. The agency's restructuring is seen as a response to the rapid changes in the global threat landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…