 Scworld
Nucleus Security Wins Multiple Awards for Vulnerability Management Solutions
Article Content

- •Nucleus Security won multiple Gold awards at the 2026 Cybersecurity Excellence Awards.
- •The company was named Best Vulnerability Management Solution at the 2026 SC Awards.
- •Nucleus 3.0 enhances vulnerability management with AI-driven insights and real-time data.
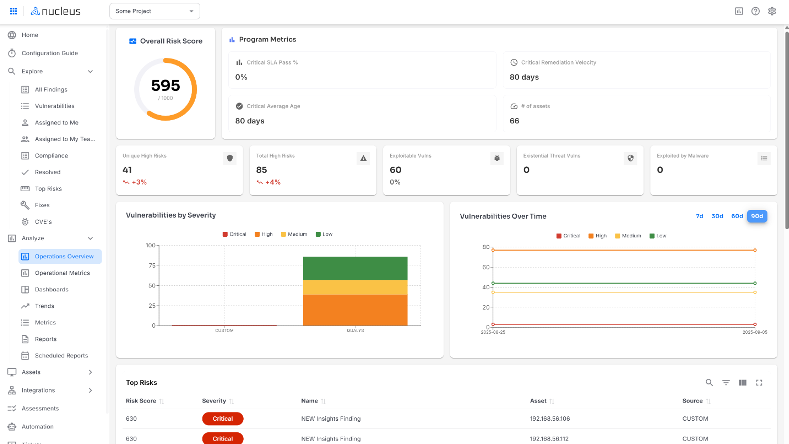
Nucleus Security has been recognized as a Gold Winner in four categories at the 2026 Cybersecurity Excellence Awards, showcasing its leadership in unified vulnerability and exposure management. The company was also awarded the Best Vulnerability Management Solution at the 2026 SC Awards for its innovative approach to transforming fragmented data into actionable insights. Nucleus Security's platform integrates data from over 200 tools, allowing organizations to manage vulnerabilities and threats effectively. Recent updates to its platform, including Nucleus 3.0, enhance its capabilities with AI-driven exposure management and real-time risk data analysis. The company serves over 500 global enterprises and government organizations, demonstrating significant improvements in risk management and remediation rates. Notable customer outcomes include a state agency reducing high-priority risks by over 60% within 90 days and a financial company achieving an 89% remediation rate across millions of findings. Nucleus Security's recognition reflects its commitment to innovation and customer satisfaction in the cybersecurity landscape.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…