 www.accessnewswire.com
Ondas Achieves EASA Certification for Advanced Missile Protection System
Article Content

- •Ondas received EASA certification for its Airborne Missile Protection System.
- •The AMPS suite protects against MANPADS and infrared-guided missile threats.
- •This certification marks a significant milestone in Ondas' defense technology expansion.
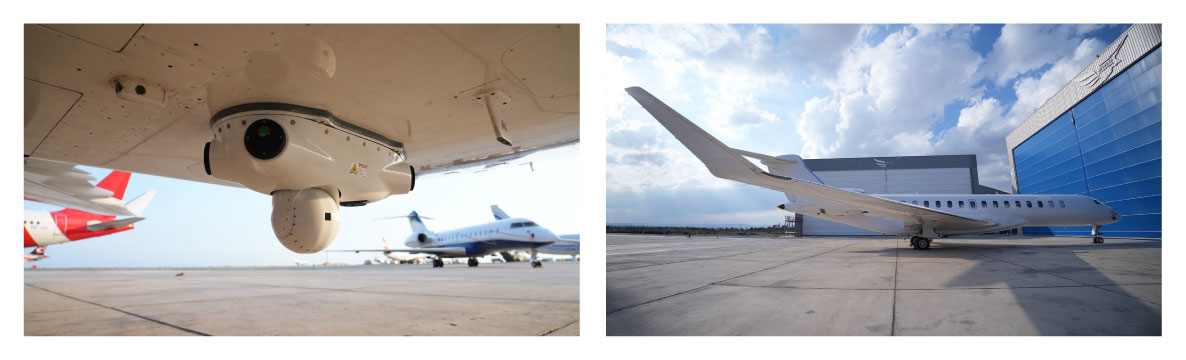
Ondas Inc. announced the successful installation and EASA certification of its Airborne Missile Protection System (AMPS) on a Bombardier Global 7500 aircraft. This certification enhances Ondas' capabilities in the global VVIP aircraft protection market, addressing the growing need for defense against sophisticated missile threats. The AMPS suite incorporates Directional Infrared Countermeasures (DIRCM) and is designed to protect against Man-Portable Air-Defense Systems (MANPADS) and other infrared-guided missile threats. The system's advanced features include missile warning, threat detection, and tracking capabilities, ensuring rapid response to missile threats. Ondas aims to leverage this certification to expand its presence in the airborne defense sector, catering to government and defense customers worldwide. The certification signifies compliance with stringent international aviation safety standards.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What aircraft is protected by the AMPS?
What threats does the AMPS protect against?
How does the AMPS enhance aircraft safety?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…