 Insurance-Edge
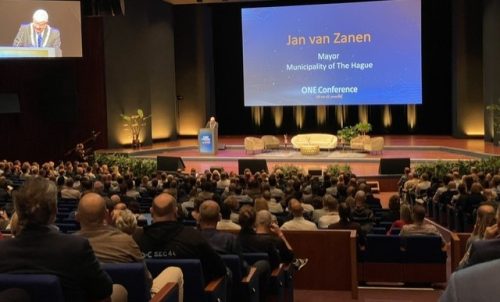
ONE Conference 2026: Collaboration Essential to Combat AI-Driven Cybercrime
Article Content

- •Collaboration among agencies is crucial to combat AI-driven cyber threats.
- •Europol's takedown of Hansa dark web site highlights vulnerabilities in organized crime.
- •Insurers could aid in tracking ransomware payments to disrupt criminal operations.
The ONE Conference 2026 in The Hague focused on the need for collaboration among law enforcement, cybersecurity experts, and insurers to tackle AI-driven cyber threats. A key discussion highlighted the takedown of the Hansa dark web marketplace by Europol, which revealed vulnerabilities in organized crime operations. The event emphasized that while takedowns are crucial, they are merely the beginning of a broader investigation that requires international cooperation. Participants noted that cybercriminals often exploit interconnected systems, making it essential for various agencies to share intelligence and resources. Insurers were suggested to play a role in tracking ransomware payments, as criminals must spend their illicit gains. The conference also featured discussions on protecting critical infrastructure from cyber threats, showcasing projects like SeaSEC aimed at enhancing maritime security. Overall, the conference underscored the importance of partnerships in addressing the evolving landscape of cybercrime.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the main focus of the ONE Conference?
What did Europol's presentation reveal?
How can insurers contribute to cybersecurity efforts?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…