 Techafricanews
Ooredoo and iQ Networks Enhance Iraq's Fibre Connectivity
Article Content

- •Ooredoo's OFN and iQ Networks signed a dark fibre agreement for Iraq connectivity.
- •The initiative aims to create a high-speed fibre corridor linking Asia, the Gulf, and Europe.
- •The project will support growing demands from AI providers and telecom operators.
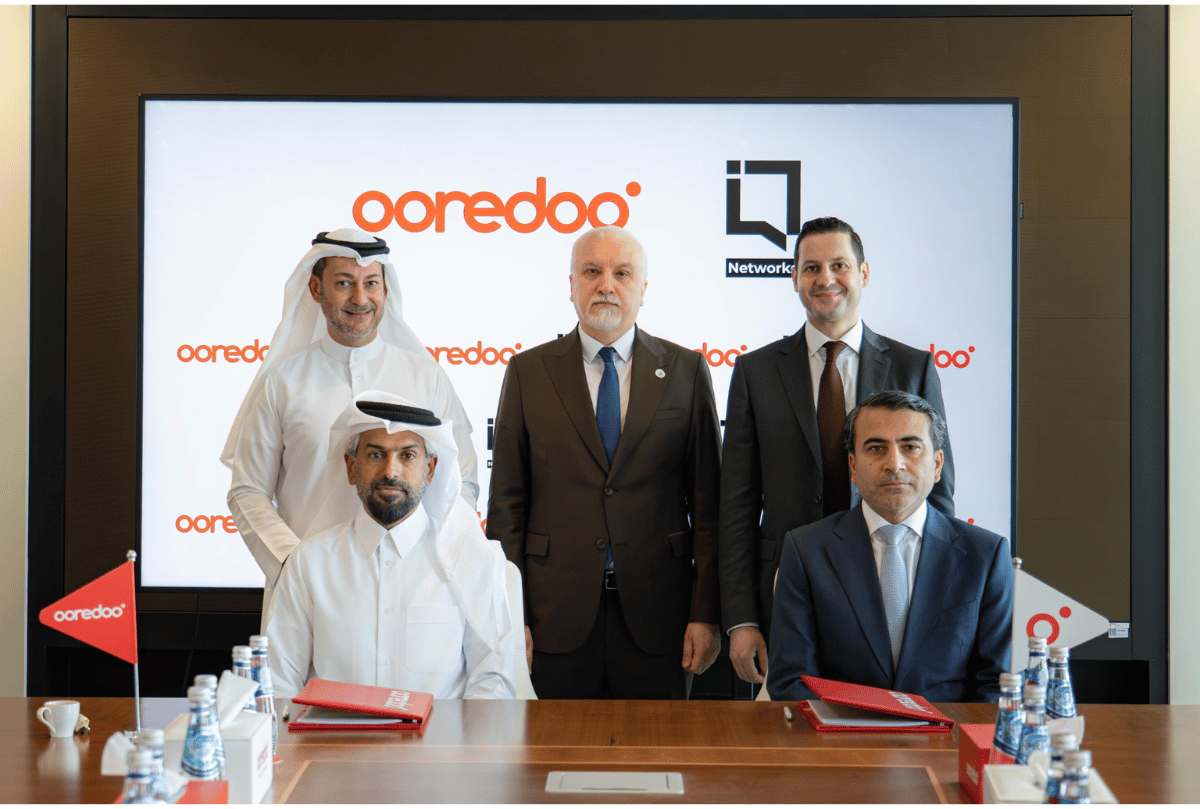
Ooredoo Group's international connectivity arm, OFN, has signed a deal with iQ Networks to purchase multiple dark fibre pairs for transit connectivity across Iraq. This agreement, alongside OFN's separate FIG landing arrangement with the Iraqi Telecommunications and Post Company (ITPC), aims to develop an integrated subsea and terrestrial connectivity corridor linking Asia, the Gulf, Iraq, and Europe. The new infrastructure will address the increasing connectivity demands from AI providers, telecom operators, hyperscalers, cloud providers, and data centres. The signing event took place at Ooredoo's headquarters in Doha, attended by key officials from Iraq's Ministry of Communications and both companies. Khalid Hassan Al-Hammadi, CEO of OFN, stated that this initiative marks a significant phase in their multi-stage infrastructure program, enhancing their international connectivity portfolio.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What is the purpose of the dark fibre agreement?
Who are the key players involved in this agreement?
What impact will this have on international data traffic?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…