 malwaretips.com
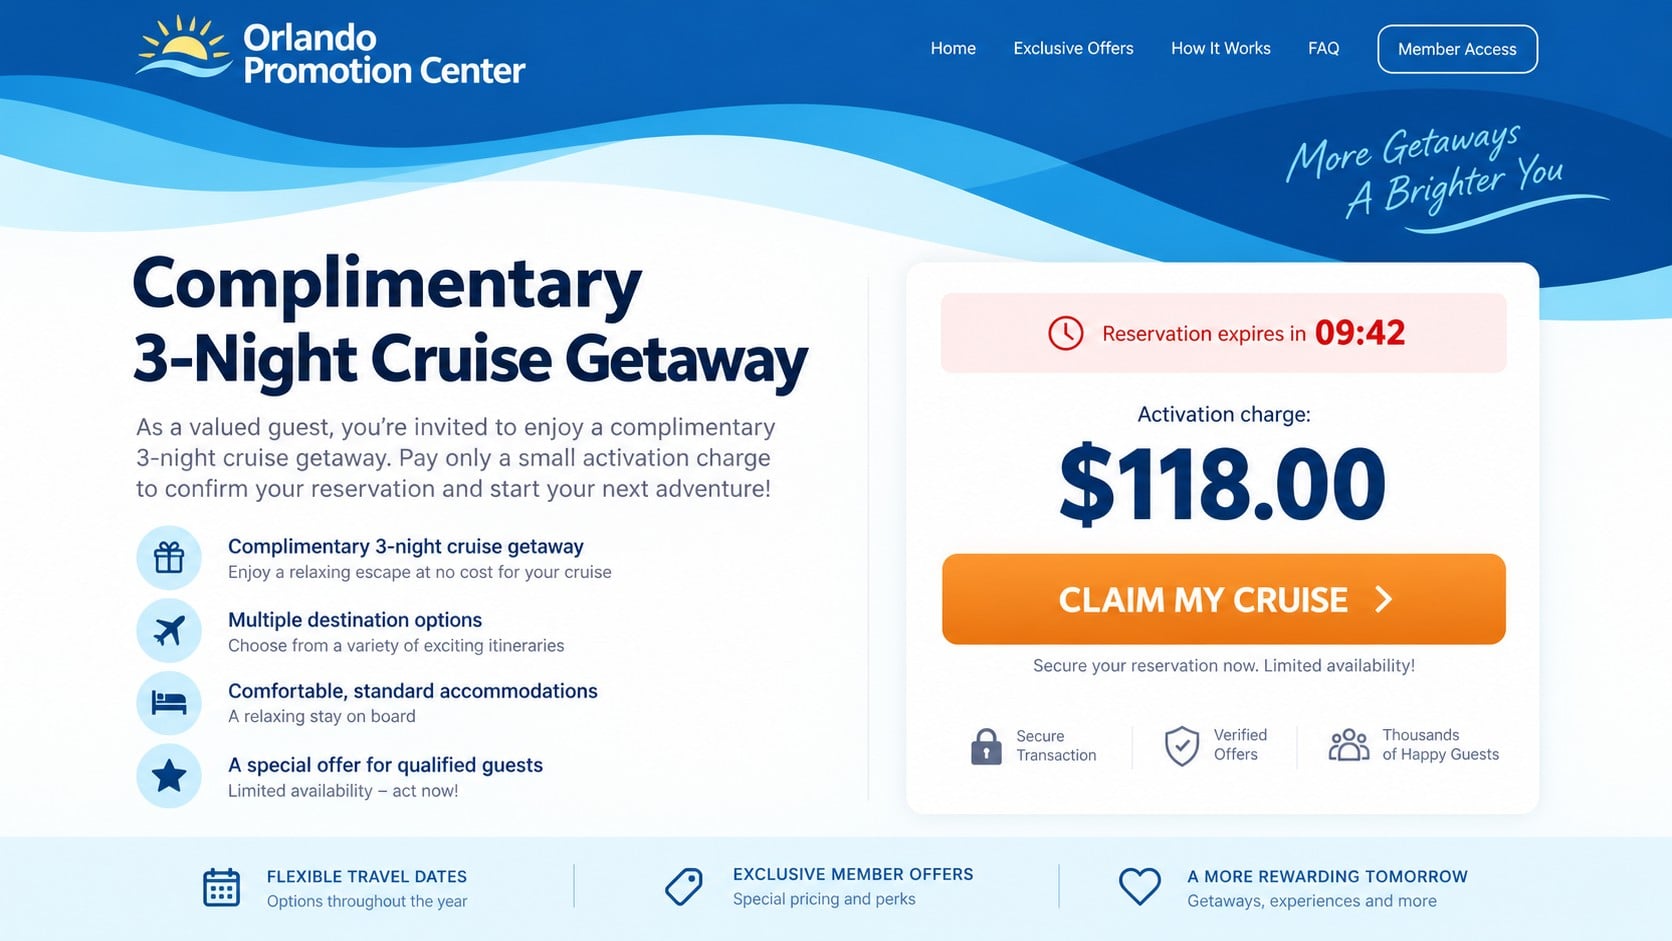
Orlando Promotion Center Free Cruise Scam Exposed
Article Content

- •The scam involves robocalls offering a 'free' cruise with hidden fees.
- •Victims are often pressured to act quickly to claim their prize.
- •No regulatory actions have been confirmed against the Orlando Promotion Center.
The Orlando Promotion Center is reportedly running a scam offering a 'free' cruise that requires upfront fees. Victims receive robocalls claiming they have been selected for a complimentary cruise, but the offer often includes hidden costs and conditions. The scam typically involves a small activation fee that does not cover all expenses associated with the trip, such as transportation and taxes. Both articles indicate that this scam has been reported frequently, with many individuals questioning its legitimacy. The Federal Trade Commission (FTC) has previously taken action against similar scams, suggesting a pattern of fraudulent behavior. Consumers are advised to be cautious and verify offers independently before providing personal information or payment. The exact ownership of the Orlando Promotion Center remains unclear, and no regulatory actions have been confirmed against it as of now.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Caribbean Cruise Line in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How can I identify this scam?
What should I do if I receive such a call?
Are there any legal actions against this scam?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 KeyDrift Malware Exploits Cisco SD-WAN Flaw CVE-2026-20127 Cisco Talos reported that the advanced persistent threat group UAT-11473 exploited a critical authentication bypass vulnerability (CVE-2026-20127) in Cisco SD-WAN Catalyst Controllers. This flaw, which has a CVSS score of 10.0, allows unauthorized remote access to administrative privileges. The group deployed a custom…