 Therecord.Media
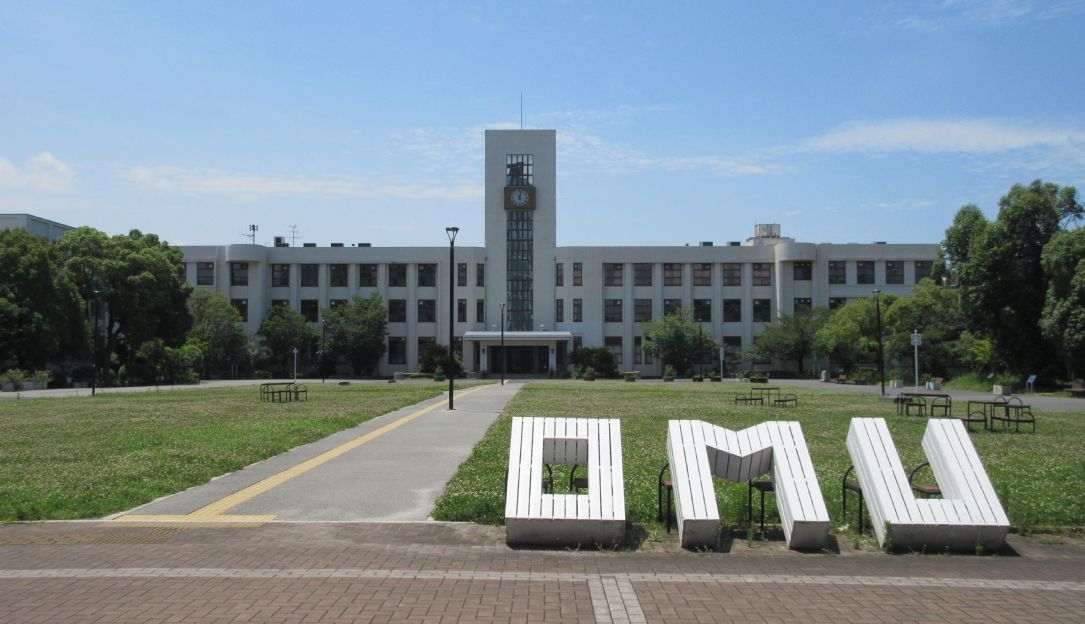
Osaka Metropolitan University Faces Ransomware Attack and Data Leak
Article Content

- •Osaka Metropolitan University canceled classes due to a suspected ransomware attack.
- •Data of at least 130,000 individuals may have been exposed, including personal information.
- •The university is investigating the incident with external cybersecurity experts.
Osaka Metropolitan University canceled classes and shut down its IT infrastructure following a suspected ransomware attack that began on October 2, 2026. The attack has rendered internal networks, email, and various administrative systems unavailable. The university reported that data belonging to at least 130,000 students and faculty may have been exposed, including names, addresses, and email addresses. Although the university has not confirmed if personal data was stolen, it is investigating the incident with cybersecurity specialists. The disruption has led to class cancellations through at least October 8, 2026, while some systems remain operational. The university has reported the incident to Japan's data protection authority and other government agencies. This incident follows a series of cyber breaches in Japan, although no connections have been established between them.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Osaka City University in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data may have been leaked?
What is the current status of classes?
Is there confirmation of data theft?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…