 ransomnews.com
Over 484,000 Exposed Cloud Buckets Found with 18 Billion Files
Article Content

- •484,142 cloud storage buckets are publicly listable, containing 18.05 billion files.
- •Amazon S3 hosts 72% of the exposed buckets, while Azure Blob shows significant over-representation in sensitive categories.
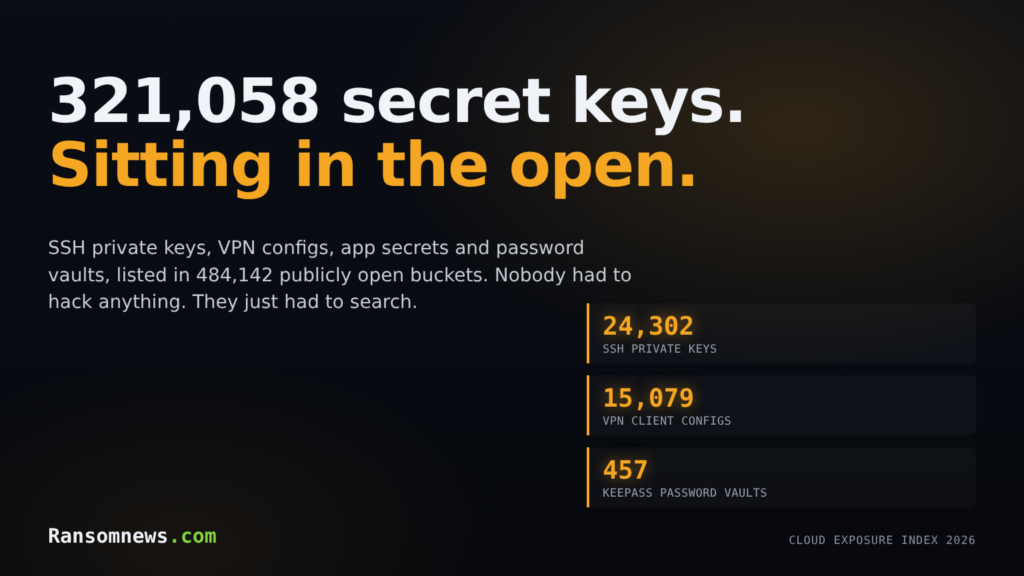
- •321,058 credential-related files are exposed, with a notable percentage of .env files modified in 2026.
The Ransomnews research team reported 484,142 publicly listable cloud storage buckets containing 18.05 billion files, including sensitive data like exposed credentials and database backups. This data was compiled using indexing engines without accessing the files themselves. Amazon S3 accounts for 72% of these exposed buckets, while Azure Blob is significantly over-represented in operational data categories such as backups and payroll records. The researchers found 321,058 files related to credentials and keys, with 67% of exposed .env files last modified in 2026. The Ransomnews Cloud Exposure Index will be updated quarterly to track changes in cloud exposure. The report indicates that many of these buckets are intentionally public, serving legitimate purposes, but highlights the risk of sensitive information being exposed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Azure in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of files are exposed?
How often will the Cloud Exposure Index be updated?
What cloud providers are most affected?
Continue Reading
 Binance Hack: $6.3 Billion Stolen in Largest Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a major security incident involving an estimated $6.3 billion in stolen funds. The attack was attributed to a compromised laptop belonging to a DevOps engineer, allowing unauthorized withdrawal transactions. Approximately $3 billion in…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…