 Securityaffairs.Co
Over 6,000 SmarterMail Servers Exposed to Critical Vulnerability
Article Content
Browse articles 
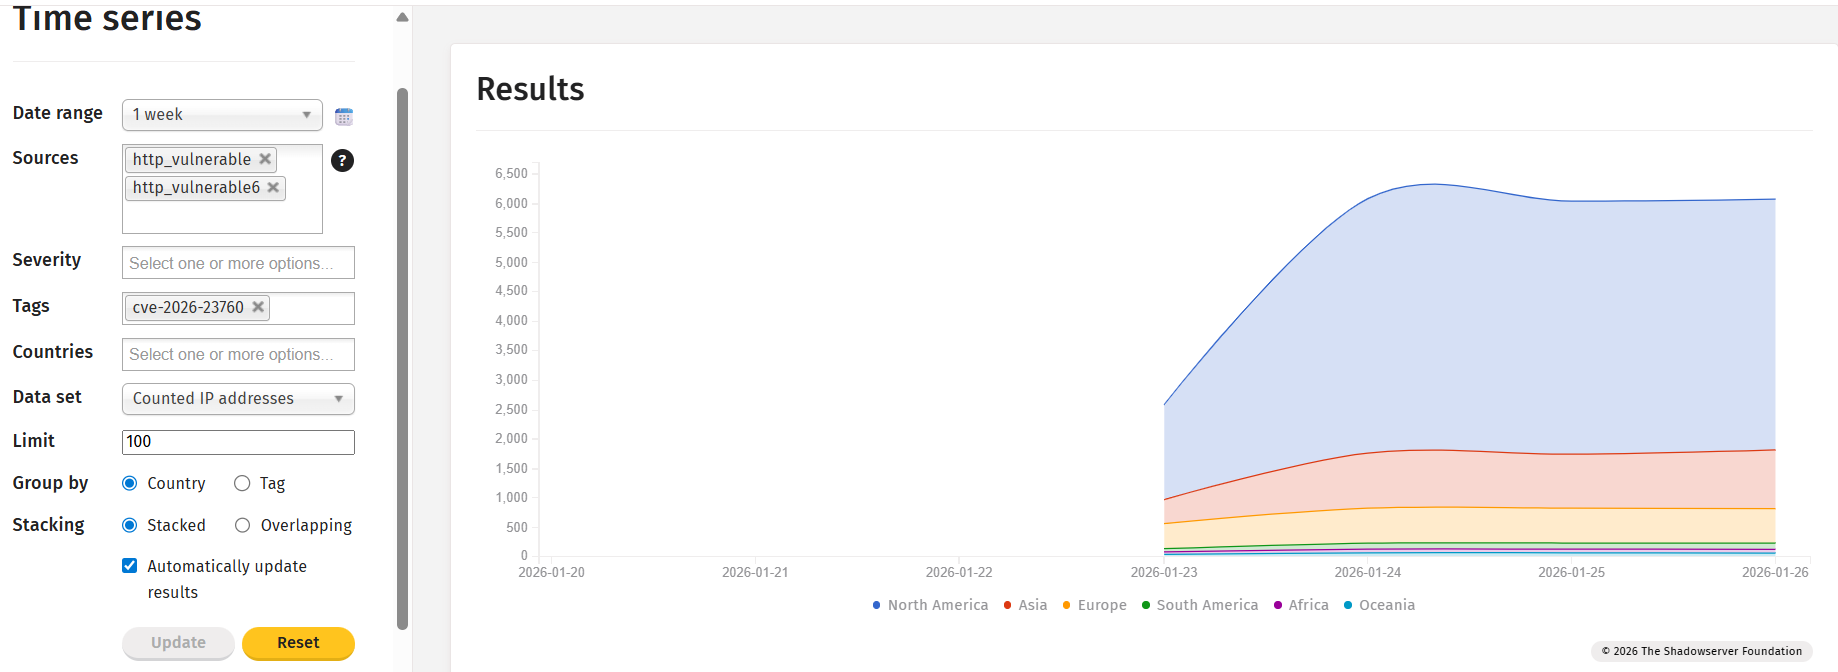
Shadowserver researchers identified over 6,000 SmarterMail servers exposed online, likely vulnerable to a critical authentication bypass flaw tracked as CVE-2026-23760. The vulnerability was disclosed by cybersecurity firm watchTowr on January 8, 2026.
Ask AI about this cluster
Answers cite the sources they use
Updated 210d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track Shadowserver and CVE-2026-23760 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2026-82039: High-Risk SQL Injection in UTMStack UTMStack versions before 11.2.16 contain a SQL injection vulnerability in the UtmAssetGroupService.searchQueryBuilder() method. This flaw allows authenticated attackers to inject arbitrary SQL through unsanitized inputs, enabling full database access and modification via the /api/utm-asset-groups/searchGroupsByFilter…
 CVE-2026-88789: High-Risk XML Vulnerability in Apache Camel Quarkus CVE-2026-88789 is a vulnerability in the XSLT support extension of Apache Camel Quarkus, affecting versions from 3.2.0 to 3.40.0. This flaw allows attackers to read local files or access internal network locations by supplying a malicious XML document with external entity declarations. The vulnerability arises from…