 Cybersecuritynews
OysterLoader Malware Loader Revealed with Rhysida Ransomware Connections
Article Content
Browse articles 
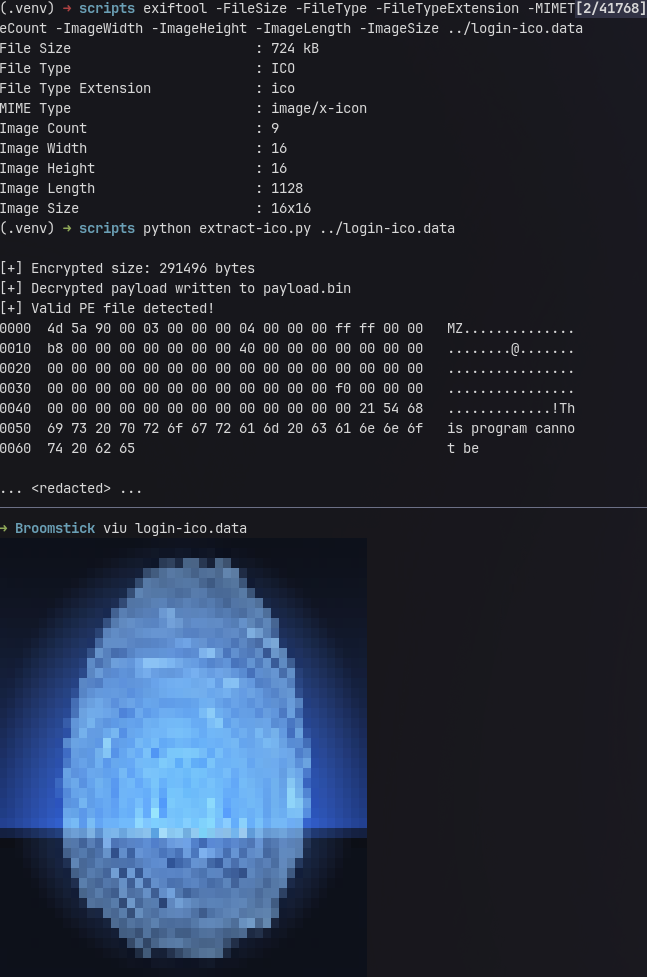
OysterLoader, a multi-stage malware loader, has been identified as a significant cybersecurity threat. First discovered in June 2024, this C++ malware employs advanced obfuscation techniques to avoid detection and is primarily distributed via counterfeit websites mimicking legitimate software applications. It has been linked to the Rhysida ransomware, further complicating the threat landscape.
Ask AI about this cluster
Answers cite the sources they use
Updated 248d ago How this analysis works
Timeline
2024-06-01
OysterLoader first identified by Rapid7
2026-02-13
OysterLoader's advanced obfuscation tactics reported
More articles in this cluster (5)
Following this threat?
Track Rhysida and OysterLoader in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Norwegian Officials' Personal Numbers Exposed on Dark Web Private phone numbers of key Norwegian officials, including Defense Minister Tore O. Sandvik and heads of military and intelligence agencies, were discovered on the dark web and Russian platforms. The leak was identified by Italian cybersecurity researcher Andrea Mavilla on November 9-10, 2026, and confirmed by…
 Anne Arundel County Faces Second Cyberattack in 18 Months Anne Arundel County, Maryland, confirmed a data breach on August 28, 2026, where hackers accessed and copied files from a limited number of government systems. The Rhysida ransomware gang claimed responsibility, threatening to leak 2.6 terabytes of documents unless a $2 million ransom is paid. County officials stated…