 Renfrewshire24
Paisley Grammar Pupils Attend Cybersecurity Career Conference
Article Content

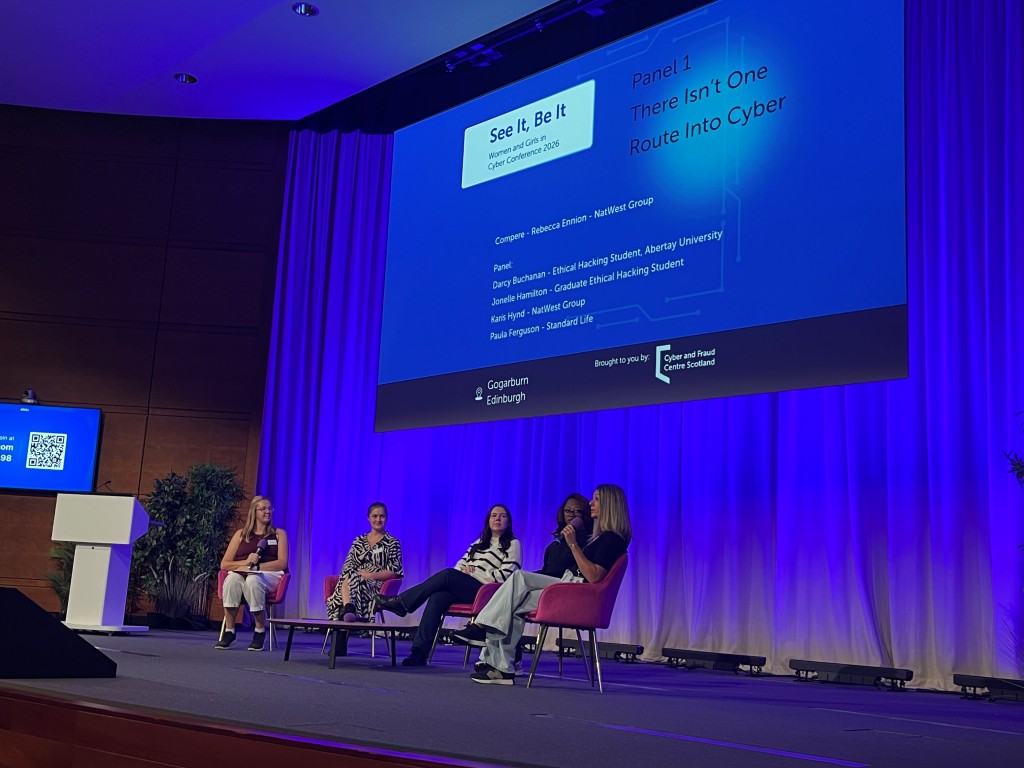
- •Paisley Grammar pupils attended the See It Be It conference on October 2, 2026.
- •The event aimed to encourage young women to pursue careers in cybersecurity.
- •Women currently make up only 16% of the UK's cybersecurity workforce.
On October 2, 2026, girls from Paisley Grammar School participated in the See It Be It conference, aimed at encouraging young women to explore careers in cybersecurity. Organized by Cyber and Fraud Centre Scotland, the event featured professionals from various sectors, including computer science and data analysis, who shared their career journeys. Shona McAlpine, a computing science teacher, emphasized the importance of connecting students' coding interests to cybersecurity careers. Despite the growing interest in technology among girls, women represent only 16% of the UK's cyber workforce. The conference aimed to address this gender imbalance and inspire students to consider diverse roles in the field. Keynote speaker Andrew Elliot discussed initiatives like the TechFirst Girls Competition to further engage young women in technology.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Cyber And Fraud Centre Scotland in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the purpose of the conference?
Who organized the See It Be It conference?
What percentage of the cybersecurity workforce is female?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…