 Nextgov
Pentagon's Zero Trust Chief Resigns Amid Cybersecurity Workforce Challenges
Article Content

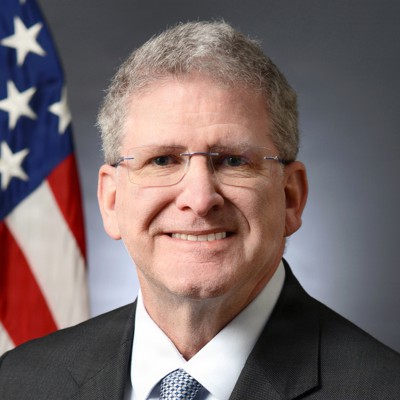
- •Randy Resnick, the Pentagon's zero trust chief, retires on October 14, 2026.
- •The Defense Department aims to meet zero trust requirements by the end of fiscal 2027.
- •Experts recommend cross-skilling existing cybersecurity personnel to address workforce gaps.
Randy Resnick, the Pentagon's top official for zero trust cybersecurity, is set to retire on October 14, 2026. His departure comes as the Defense Department pushes to meet zero trust requirements by the end of fiscal 2027. Resnick has been instrumental in developing the framework for zero trust across military networks, emphasizing continuous verification and tighter controls to protect sensitive data. The articles highlight ongoing challenges in the cybersecurity workforce, with experts advocating for cross-skilling existing employees rather than solely hiring new talent. The government faces significant cybersecurity challenges, including the implementation of zero trust architectures and AI security. The current workforce gap in cybersecurity skills is a critical issue that needs addressing to ensure effective defense against cyber threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is zero trust?
Why is the cybersecurity workforce gap a concern?
What should organizations do to improve their cybersecurity workforce?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…