 cofense.com
Phishing Campaign Exploits Anthropic AI to Steal Credentials
Article Content

- •Phishing emails impersonating Anthropic target Google and Microsoft accounts.
- •Attackers use URL shorteners and CAPTCHAs to bypass email security tools.
- •The campaign has been active since September 2026, with ongoing spoofing tactics.
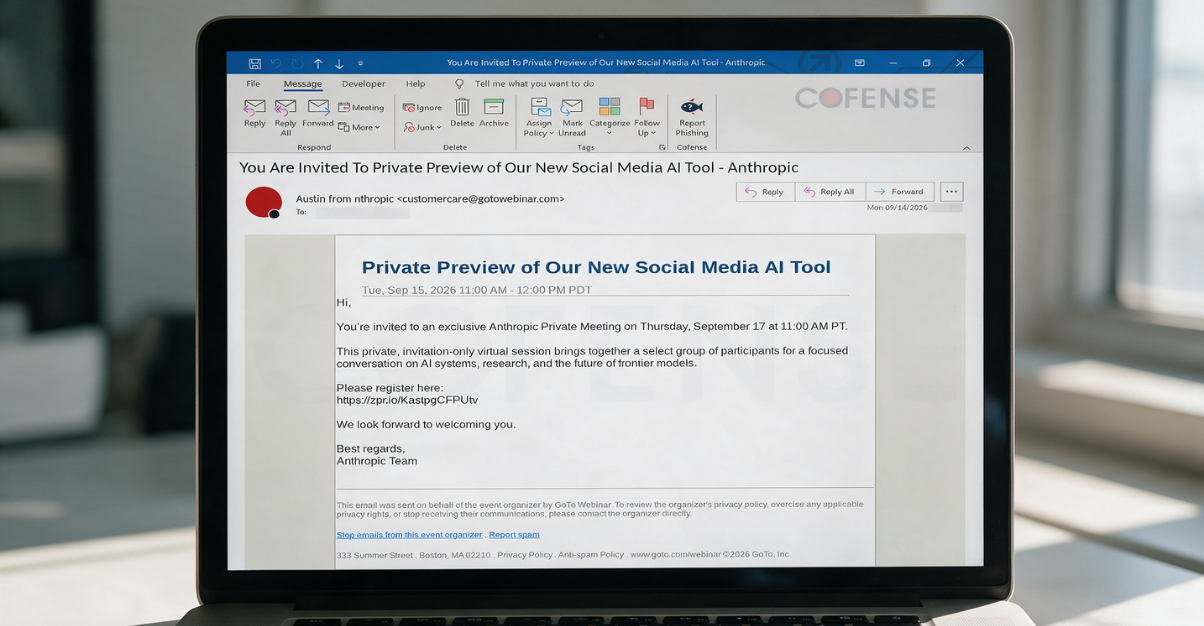
Since September 2026, attackers have been sending phishing emails impersonating Anthropic, aiming to steal Google and Microsoft account credentials. The emails, which promise exclusive access to a new AI tool, contain multiple red flags, including grammatical errors and incorrect sender information. Despite these obvious signs, the emails have bypassed leading secure email gateways due to the use of URL shorteners and CAPTCHAs. Victims who click the links are directed to a fake Zoom meeting page, where they may inadvertently provide their login credentials. Cofense has noted that the campaign's inept tactics raise questions about how it evaded spam filters. The threat actor has also begun spoofing Anthropic's website, indicating possible use of AI in the campaign. Organizations are urged to remain vigilant against such phishing attempts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Following this threat?
Track Google in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How can we identify these phishing emails?
What should we do if an employee clicks the link?
Are there any specific tools to help mitigate this threat?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…