 Malwarebytes
Phishing Scam Exploits Claude Max Giveaway to Steal Google Credentials
Article Content

- •The phishing scam offers fake Claude Max subscriptions to lure victims.
- •It uses a convincing browser-in-the-browser technique to capture Google credentials.
- •Malwarebytes researchers have confirmed the scam's existence and are investigating its reach.
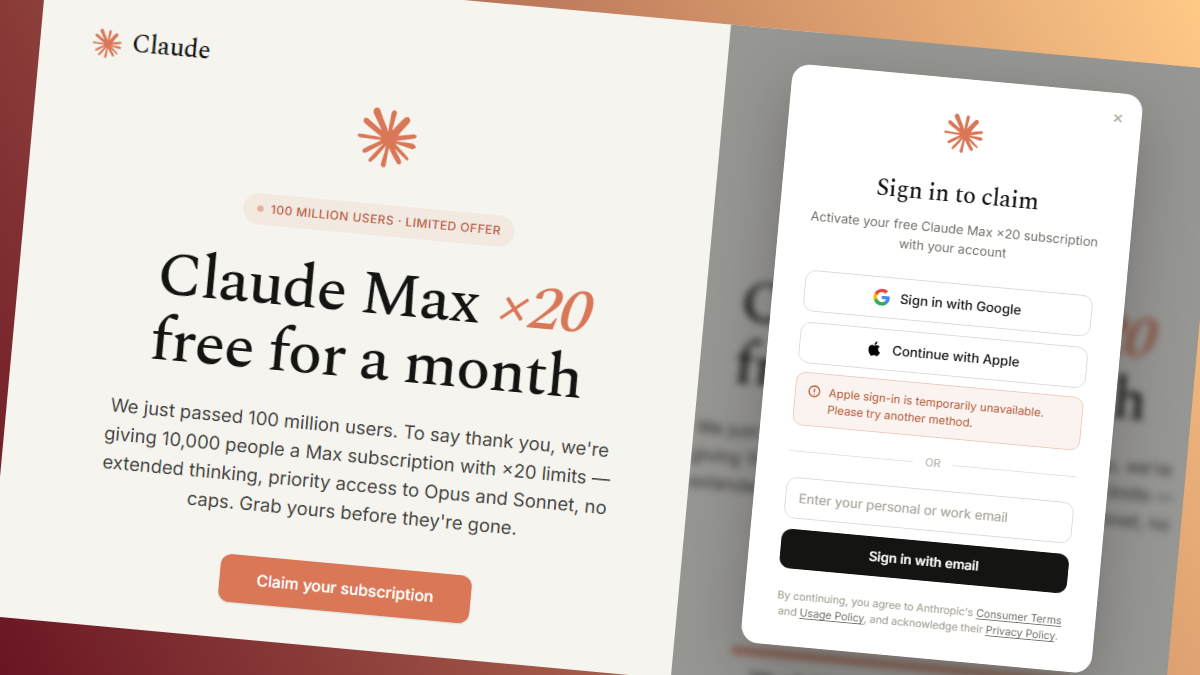
A new phishing campaign has emerged, masquerading as a giveaway of Anthropic's Claude Max service. The scam claims to offer 10,000 free one-month subscriptions to users, leveraging the popularity of AI services. Users are directed to a spoofed Google sign-in page designed to capture their login credentials. The phishing site mimics Claude's branding and creates a sense of urgency with a countdown timer. It does not request payment details, which makes it more convincing. The attack method uses a 'browser-in-the-browser' technique, creating a fake Google sign-in window within the existing browser tab. This method has been documented since 2022 and poses significant risks to users' Google accounts and any linked services. The campaign has been reported by Malwarebytes, with researchers noting its sophisticated design. As of now, the extent of the scam's reach is still being investigated.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (19)
Following this threat?
Track Anthropic in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…