 Fortune
Phishing Training Ineffective as 23% Lack MFA Adoption
Article Content

- •82% of surveyed professionals received phishing training, but 23% lack MFA.
- •88% of respondents believe their organizations are secure despite vulnerabilities.
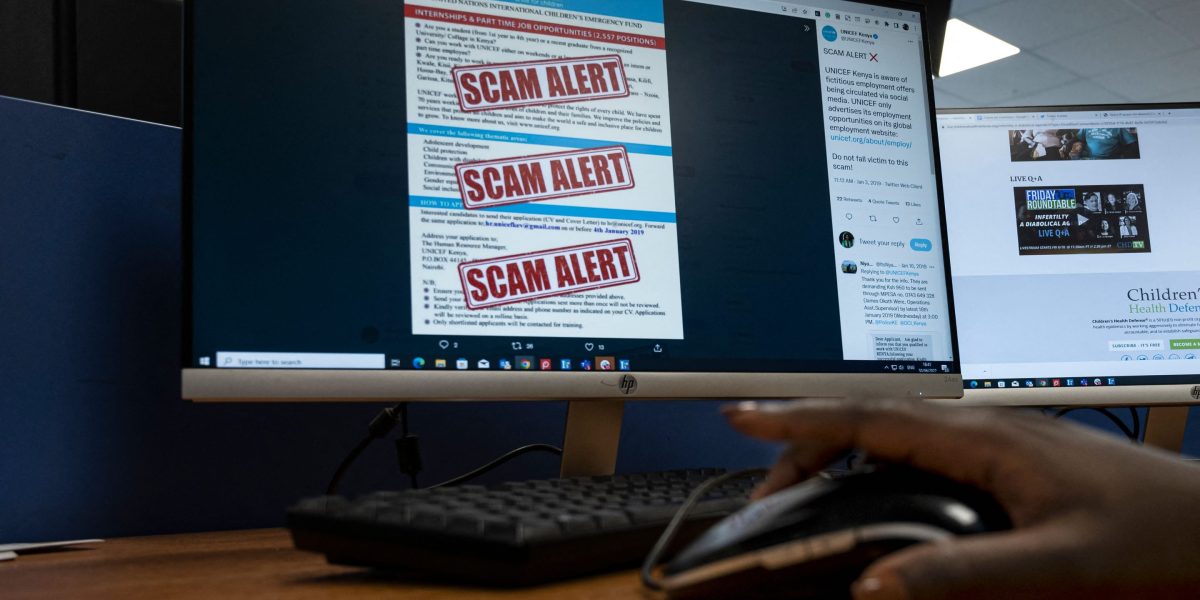
- •Phishing attacks can exploit real needs, making them harder to detect.
A recent survey by Yubico and Okta revealed that while 82% of 1,890 technology and security professionals received phishing training, 23% of their organizations do not enforce multifactor authentication (MFA). Despite this, 88% of respondents consider their enterprises secure. The survey, conducted from July 2 to 16, 2026, highlights a gap in the adoption of security measures rather than awareness of phishing threats. Experts suggest that even well-trained employees can fall victim to scams, especially when messages appear legitimate and urgent. The findings indicate a need for organizations to implement stronger security protocols beyond training sessions to mitigate phishing risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What percentage of organizations lack MFA?
How many professionals received phishing training?
What is the main issue identified in the survey?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…