 www.plymouthplus.co.uk
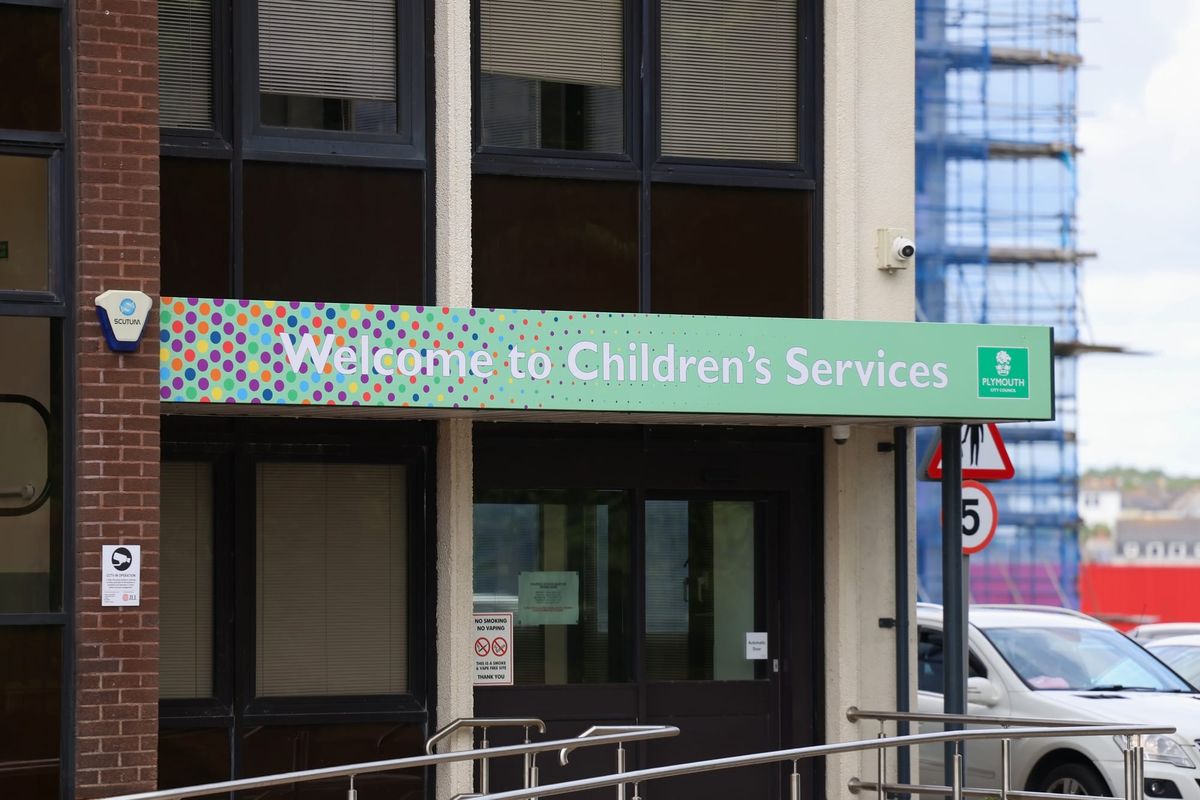
Plymouth City Council Exposes Email Addresses of 500 Families in Data Breach
Article Content

- •Plymouth City Council exposed email addresses of around 500 families due to a BCC error.
- •The incident was reported to the Information Commissioner's Office, which closed the case with no further action.
- •The council plans to implement additional checks to prevent similar breaches in the future.
Plymouth City Council mistakenly revealed the email addresses of approximately 500 families in a mass email due to human error. The email, sent by the Elective Education team, was intended to inform families about upcoming legislative changes but failed to use the BCC function. This incident follows a similar breach by City of York Council, highlighting ongoing issues with email privacy in public sector communications. The council has since apologized and reported the incident to the Information Commissioner's Office (ICO), which closed the case after providing data protection advice. The council has committed to implementing additional checks to prevent future occurrences. While no sensitive personal information was disclosed, the incident serves as a reminder of the risks associated with basic email functionalities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track City Of York Council in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…