 Hindustantimes
PM Modi Highlights Cybersecurity Threats to India's Banking System
Article Content

- •PM Modi inaugurated RBI's data centre and Cybersecurity Training Institute in Bhubaneswar.
- •He warned that modern warfare includes economic attacks via cyber threats.
- •Over half of India's population was excluded from banking until 2014, according to Modi.
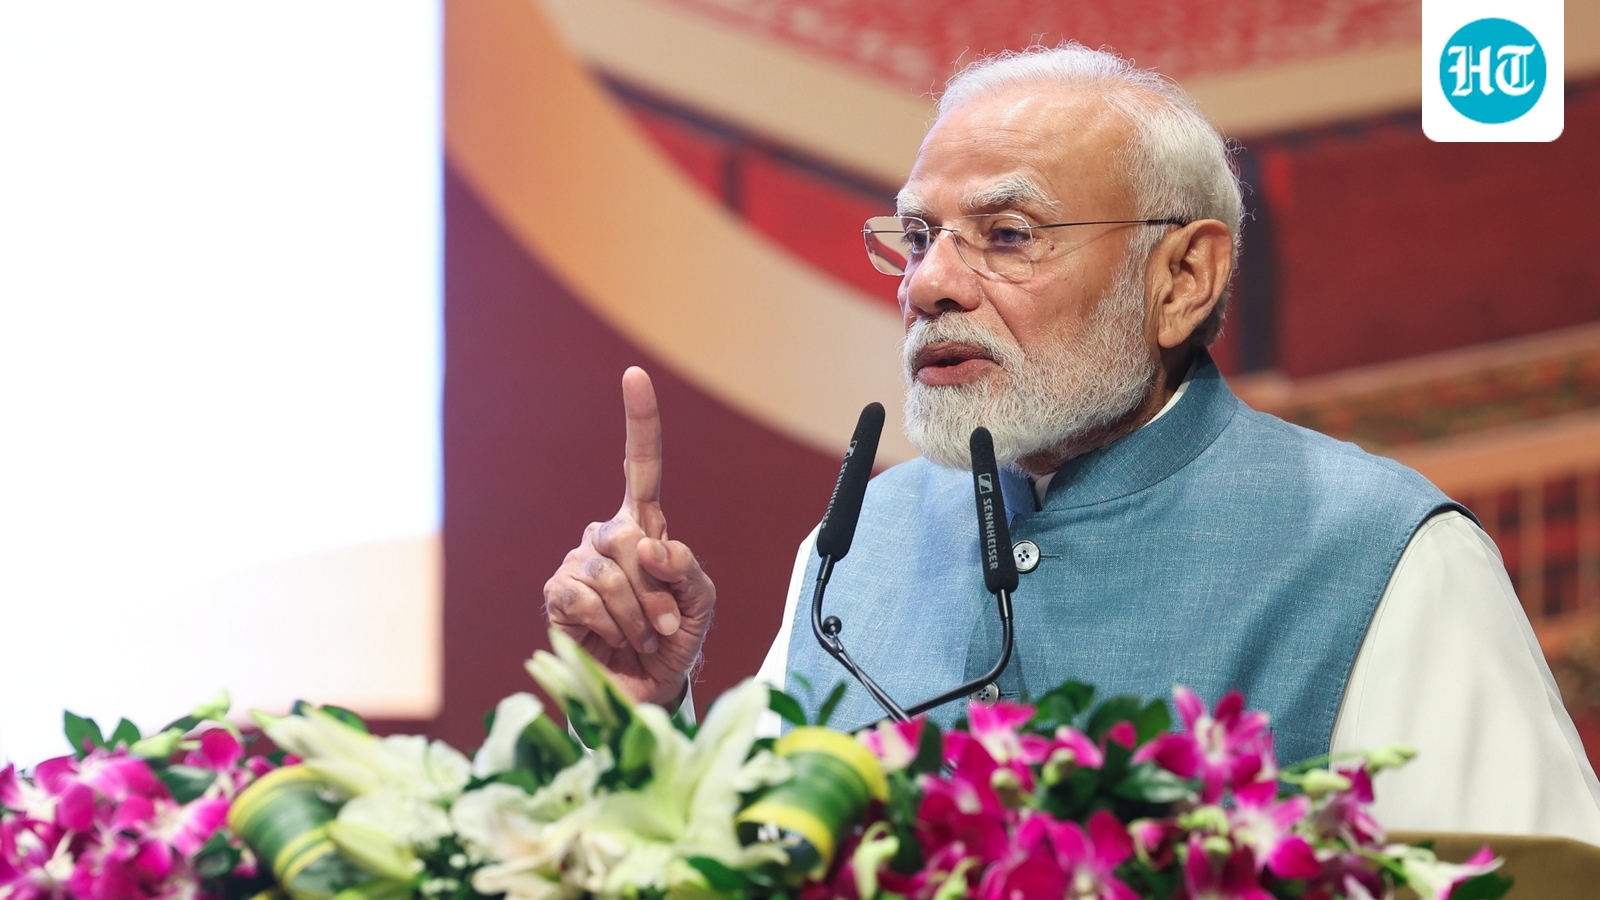
On October 25, 2026, Prime Minister Narendra Modi inaugurated the Reserve Bank of India's new data centre and Cybersecurity Training Institute in Bhubaneswar. He emphasized that modern warfare extends beyond traditional weapons, highlighting the need to protect financial institutions from cybercriminals and cyberterrorists. Modi stated that as India's economy grows, safeguarding the banking system is essential. He criticized past Congress governments for limiting banking access to select groups, leaving over half the population outside the banking ecosystem until 2014. The Prime Minister called for modern infrastructure and a skilled workforce to tackle evolving cyber threats. The new facilities aim to enhance the security and resilience of India's banking infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Reserve Bank Of India in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific threats are being addressed?
What infrastructure improvements are planned?
How has banking access changed since 2014?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…