 www.f5.com
Post-Quantum Cryptography Readiness Lags Despite CDN Adoption
Article Content

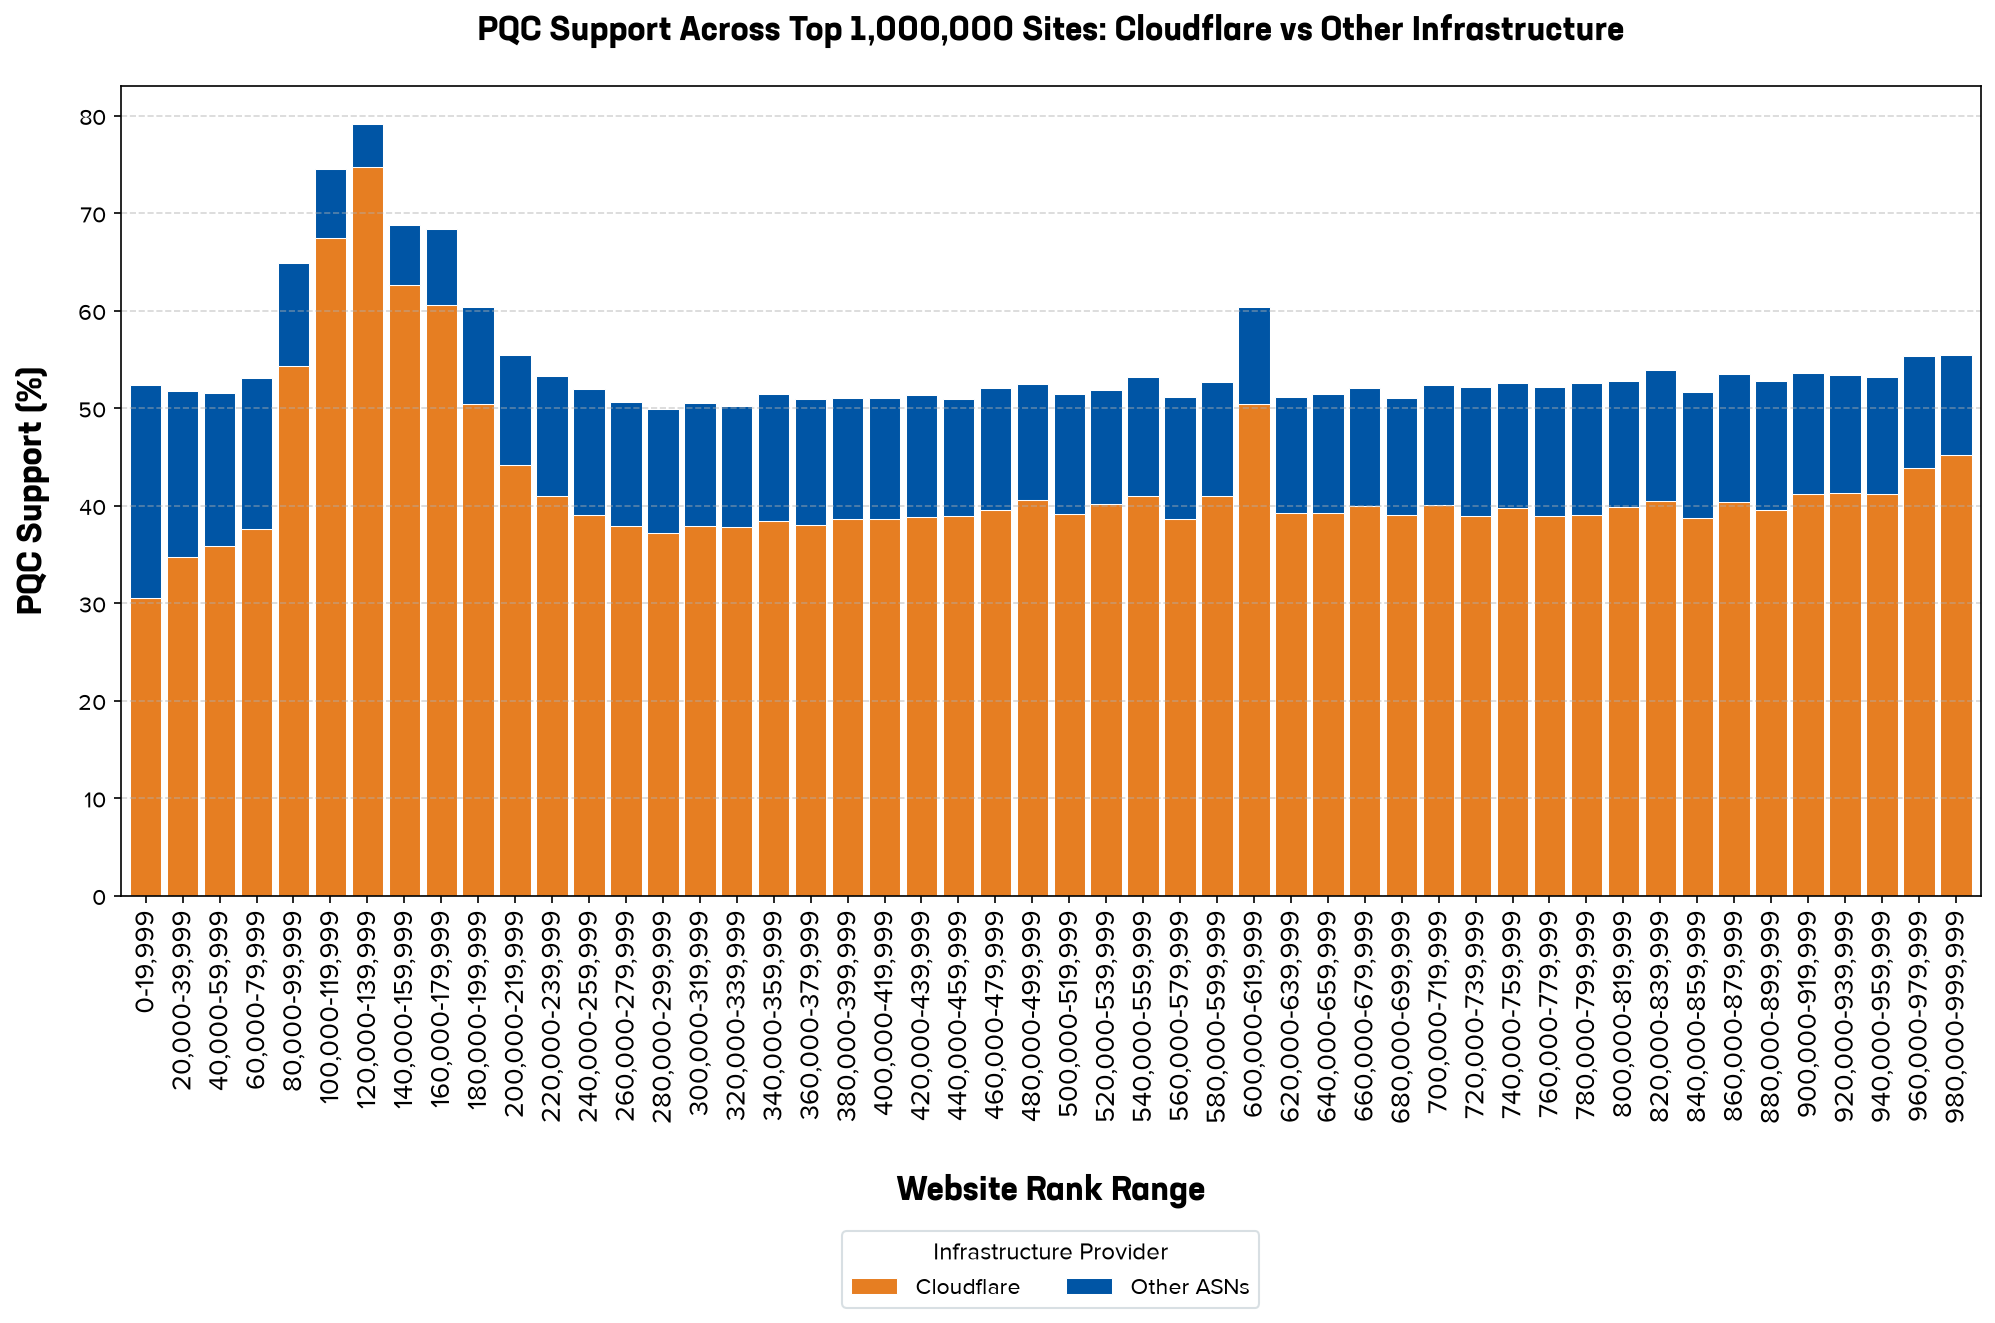
- •54% of top websites support PQC, mainly due to CDN providers.
- •Only 27% of CISOs are implementing PQC actively within their organizations.
- •True quantum readiness requires upgrades beyond just front-end protections.
As of October 2026, over half (54%) of the top 1 million websites support post-quantum key exchange (PQC), primarily due to content delivery networks (CDNs) enabling this feature by default. However, only 27% of Chief Information Security Officers (CISOs) report actively implementing PQC within their organizations. The F5 Labs report indicates that true quantum readiness requires comprehensive upgrades across all technology layers, not just front-end protections. Experts warn that internal connections remain vulnerable to potential attacks, as many organizations have not upgraded their internal infrastructure. CISA and the G7 Cyber Security Working Group have called for a focus on integrating PQC into cybersecurity requirements and procurement processes. The report highlights that while edge adoption is a positive step, it does not equate to overall enterprise readiness. The need for organizations to engage with vendors about their quantum security plans is emphasized, as many third-party dependencies could complicate migration efforts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
What percentage of websites support PQC?
What are the main challenges in PQC implementation?
How can organizations prepare for quantum threats?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…