 News.Ycombinator
Proton Meet's Privacy Claims Under Scrutiny Due to US CLOUD Act Compliance
Article Content

- •Proton Meet is marketed as a privacy-focused video conferencing tool.
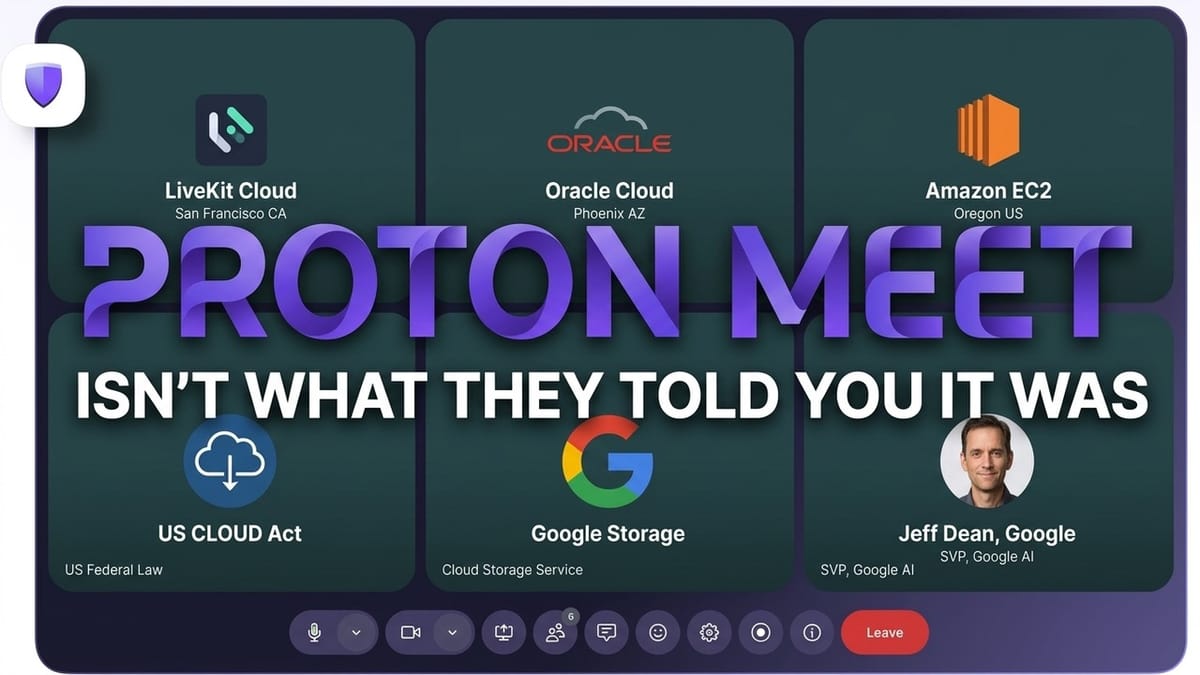
- •The service relies on LiveKit Cloud, which is subject to the US CLOUD Act.
- •Proton's claims of end-to-end encryption may be undermined by its infrastructure choices.
Proton has launched a new video conferencing service called Proton Meet, marketed as a privacy-focused alternative to mainstream platforms. While Proton claims that Meet provides end-to-end encryption and complies with GDPR and CCPA, an investigation reveals that the service relies heavily on LiveKit Cloud, a US-based infrastructure subject to the US CLOUD Act. This raises concerns about data privacy and compliance, as the CLOUD Act allows US authorities to access data stored by US companies regardless of where the data is physically located. The architecture includes a Swiss-controlled key exchange but ultimately depends on American servers for media transmission. Proton's marketing emphasizes privacy, yet the underlying infrastructure may compromise these claims. The service is free for one-hour meetings with up to 50 participants, but a pro plan is available for longer calls. The implications of using Proton Meet could affect organizations that prioritize data protection and compliance with international privacy laws.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…