 Teiss
Ransomware Attack Targets University of Illinois Chicago's College of Medicine
Article Content

- •Ransomware attack by Booba group affects UIC's College of Medicine.
- •344 gigabytes of data reportedly stolen; investigation ongoing.
- •No impact on main university network or patient care delivery.
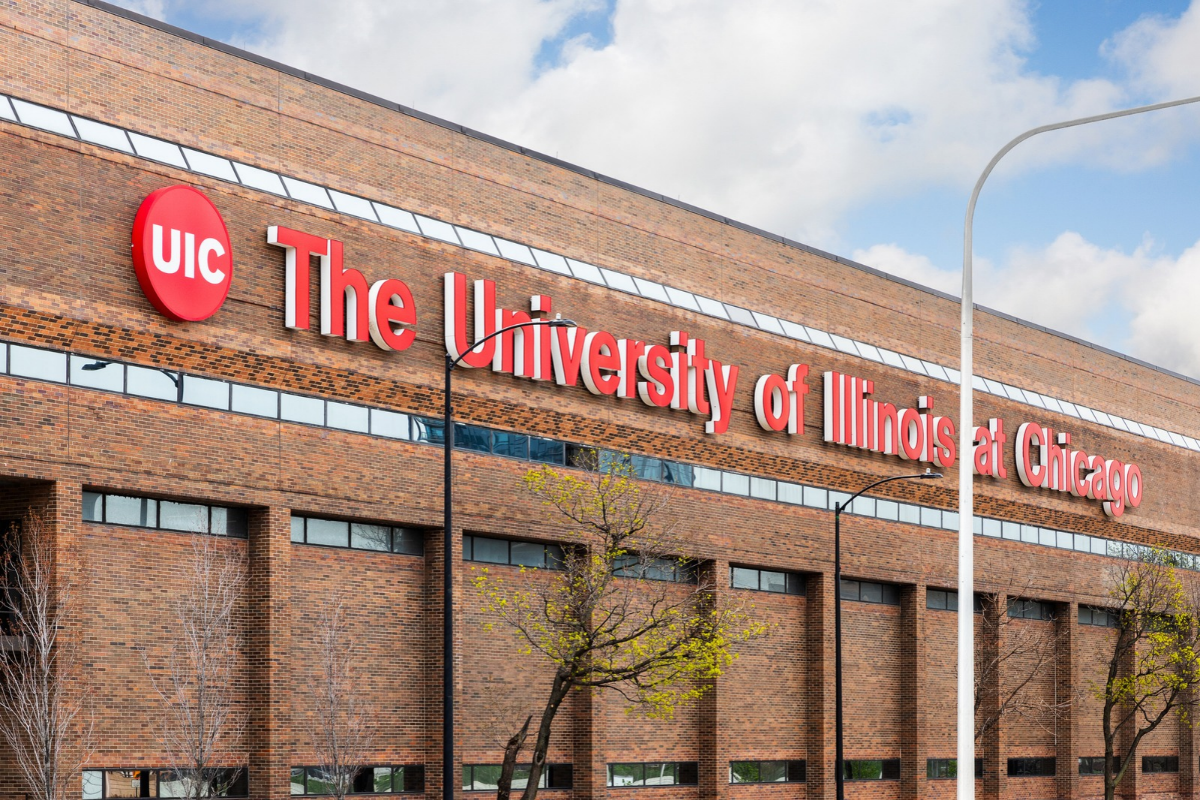
The University of Illinois Chicago (UIC) reported a ransomware attack affecting its College of Medicine, which limited access to some systems and resulted in data theft. The attack was attributed to a ransomware group named Booba, which claimed to have stolen 344 gigabytes of data. UIC's IT staff activated incident response protocols and engaged cybersecurity experts to investigate the breach. Affected systems have since been restored, and the university confirmed that its main network and patient care delivery were not impacted. The university is conducting a forensic investigation to determine the extent of compromised data, including personal, research, or academic information. Law enforcement has been notified, and UIC plans to inform affected individuals once the investigation concludes. Booba has been active since July 2026 and has claimed responsibility for 49 attacks to date.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Booba and Merrimack County in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was stolen in the attack?
How is UIC responding to the attack?
Will affected individuals be notified?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…