 Concordmonitor
Ransomware Targets Backup Systems: Merrimack County Avoids Ransom Payment
Article Content

- •Merrimack County avoided a ransom payment due to effective backup systems.
- •The cyberattack occurred in late August 2026, impacting several county services.
- •Details of the attack remain limited, with no confirmed use of AI or phishing.
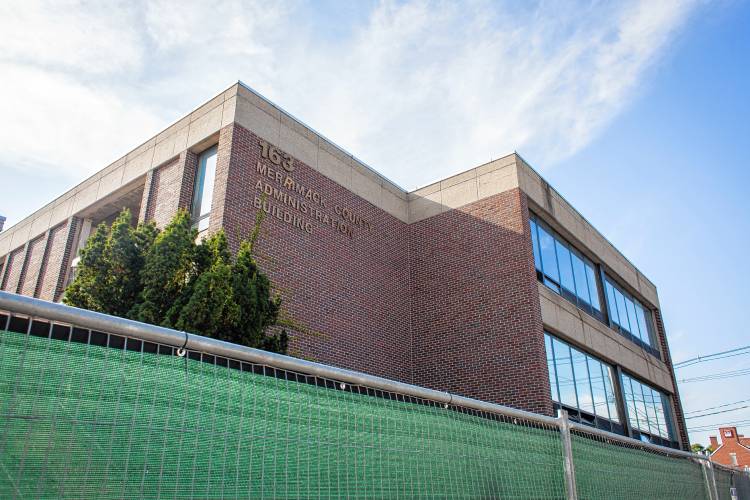
Merrimack County experienced a ransomware cyberattack in late August 2026 that disrupted services. County Administrator Ross Cunningham confirmed that their backup systems allowed them to restore operations without paying a ransom. The specific details of the attack remain limited, and there is no indication of AI or phishing involvement. The incident highlights the importance of maintaining robust backup systems to mitigate ransomware threats. The county's Register of Deeds office was notably affected, unable to accept electronic submissions for weeks. The attack's vector and the identity of the threat actors have not been disclosed, and the investigation is ongoing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track BlackCat and Change Healthcare in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What happened to Merrimack County?
How did the county avoid paying ransom?
What details are known about the attack?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…