 Thehackernews
RatHat Android Malware Uses AI for Persistent Control and Data Theft
Article Content

- •RatHat malware uses AI for automated device control and evasion of detection.
- •It exploits Accessibility permissions to gain shell-level access on Android devices.
- •The malware employs multiple anti-analysis techniques to complicate detection efforts.
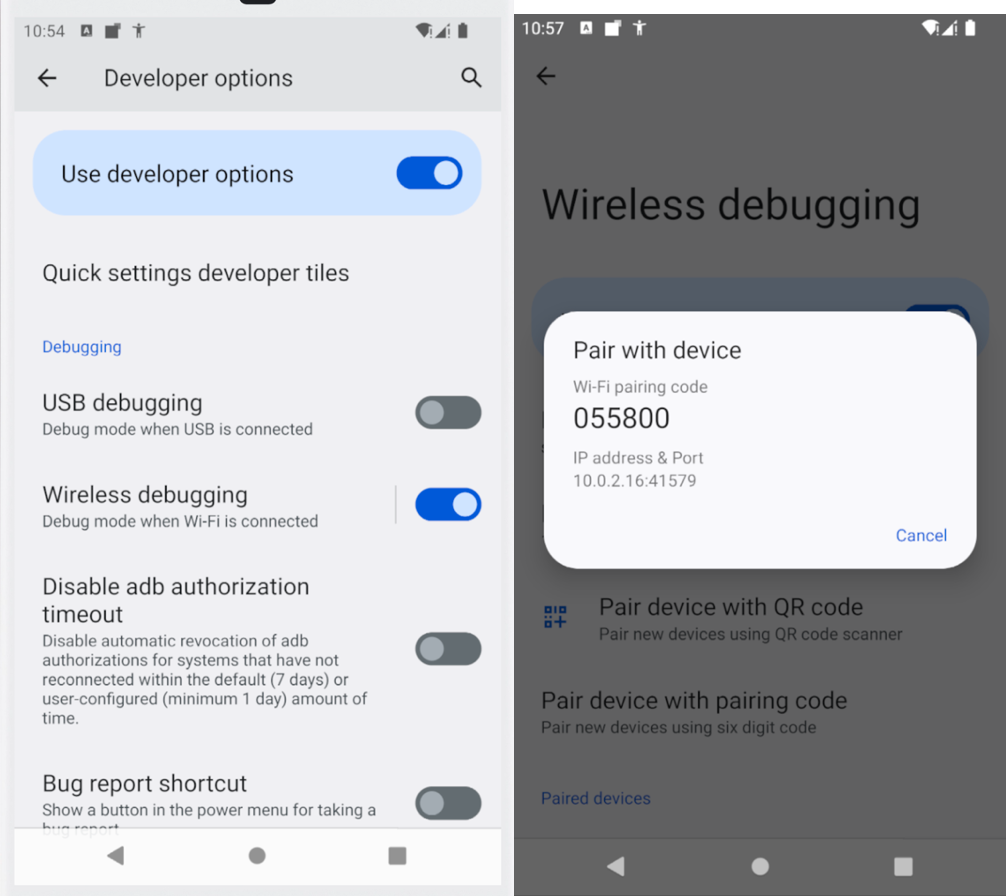
Cybersecurity researchers have identified a new Android malware named RatHat, believed to be operated by China-based threat actors. This malware exploits Android's Accessibility permissions and uses an AI-powered subsystem to automate device control, making it harder to detect. RatHat is distributed through targeted smishing and malvertising campaigns, leading users to install malicious APKs from deceptive sources. Once installed, it can enable Developer Options and Wireless Debugging to gain shell-level access without external devices. The malware features multiple anti-analysis techniques to evade detection and can intercept SMS messages, capture credentials, and display fake overlays for banking apps. It is designed to maintain persistence even after attempts to uninstall it. Zimperium researchers have linked the malware to Chinese threat actors based on the use of Chinese language prompts in its code.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ToxicPanda and RatHat in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 ToxicPanda 2.0 Expands Android Banking Attacks to 16 Countries ToxicPanda 2.0 has been upgraded to target 349 financial applications across 16 countries, significantly expanding its reach beyond Europe. The malware exploits Android Wireless Debugging to gain unauthorized access to devices and steal banking credentials. This version of ToxicPanda represents a shift from a…
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…