 Ynetnews
Renewed Activity at Iranian Nuclear Site Post-Israeli Strike
Article Content

- •Satellite images show renewed activity at the Minzadehei nuclear site in Iran.
- •The site was heavily damaged by Israeli airstrikes in March 2026.
- •Ongoing cleanup and construction efforts indicate Iran's attempt to restore nuclear capabilities.
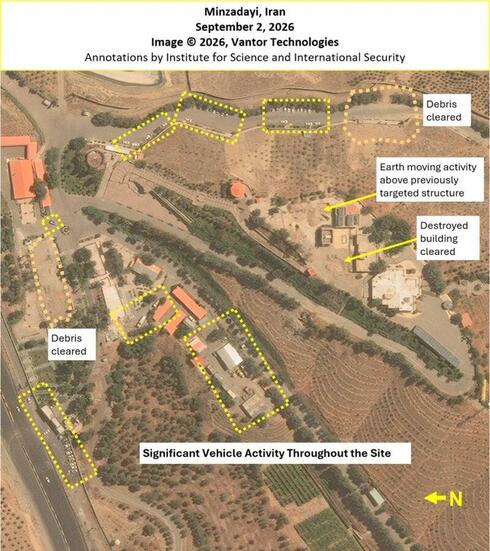
Recent satellite images reveal significant renewed activity at the Minzadehei nuclear site in Iran, which was struck by Israel during Operation Roaring Lion in March 2026. High-resolution imagery from VANTOR Technologies shows regular vehicle traffic and ongoing earthworks at the site, indicating efforts to restore nuclear weapons development capabilities. The Institute for Science and International Security reported that the site had been heavily damaged, with several buildings and underground structures destroyed. Cleanup operations have been observed, including debris removal and repairs to the hillside. This activity suggests Iran is attempting to reestablish its nuclear program after the Israeli attack. The IDF previously identified the site as linked to nuclear weapons development, and intelligence indicated that Iranian scientists were present before the strike. The renewed activity coincides with other reports of Iran rebuilding its nuclear infrastructure at various locations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What is the current status of the Minzadehei site?
What was the impact of the Israeli airstrike?
Are there any indications of nuclear material being processed?
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…