 Itpro
Rising Threat from North Korean Fake IT Worker Schemes
Article Content

- •North Korean operatives are using deepfake technology to create convincing fake job candidates.
- •The WaterPlum group has infected over 30,000 devices and stolen $10.7 million.
- •Organizations worldwide are increasingly targeted, with a focus on sectors like software and healthcare.
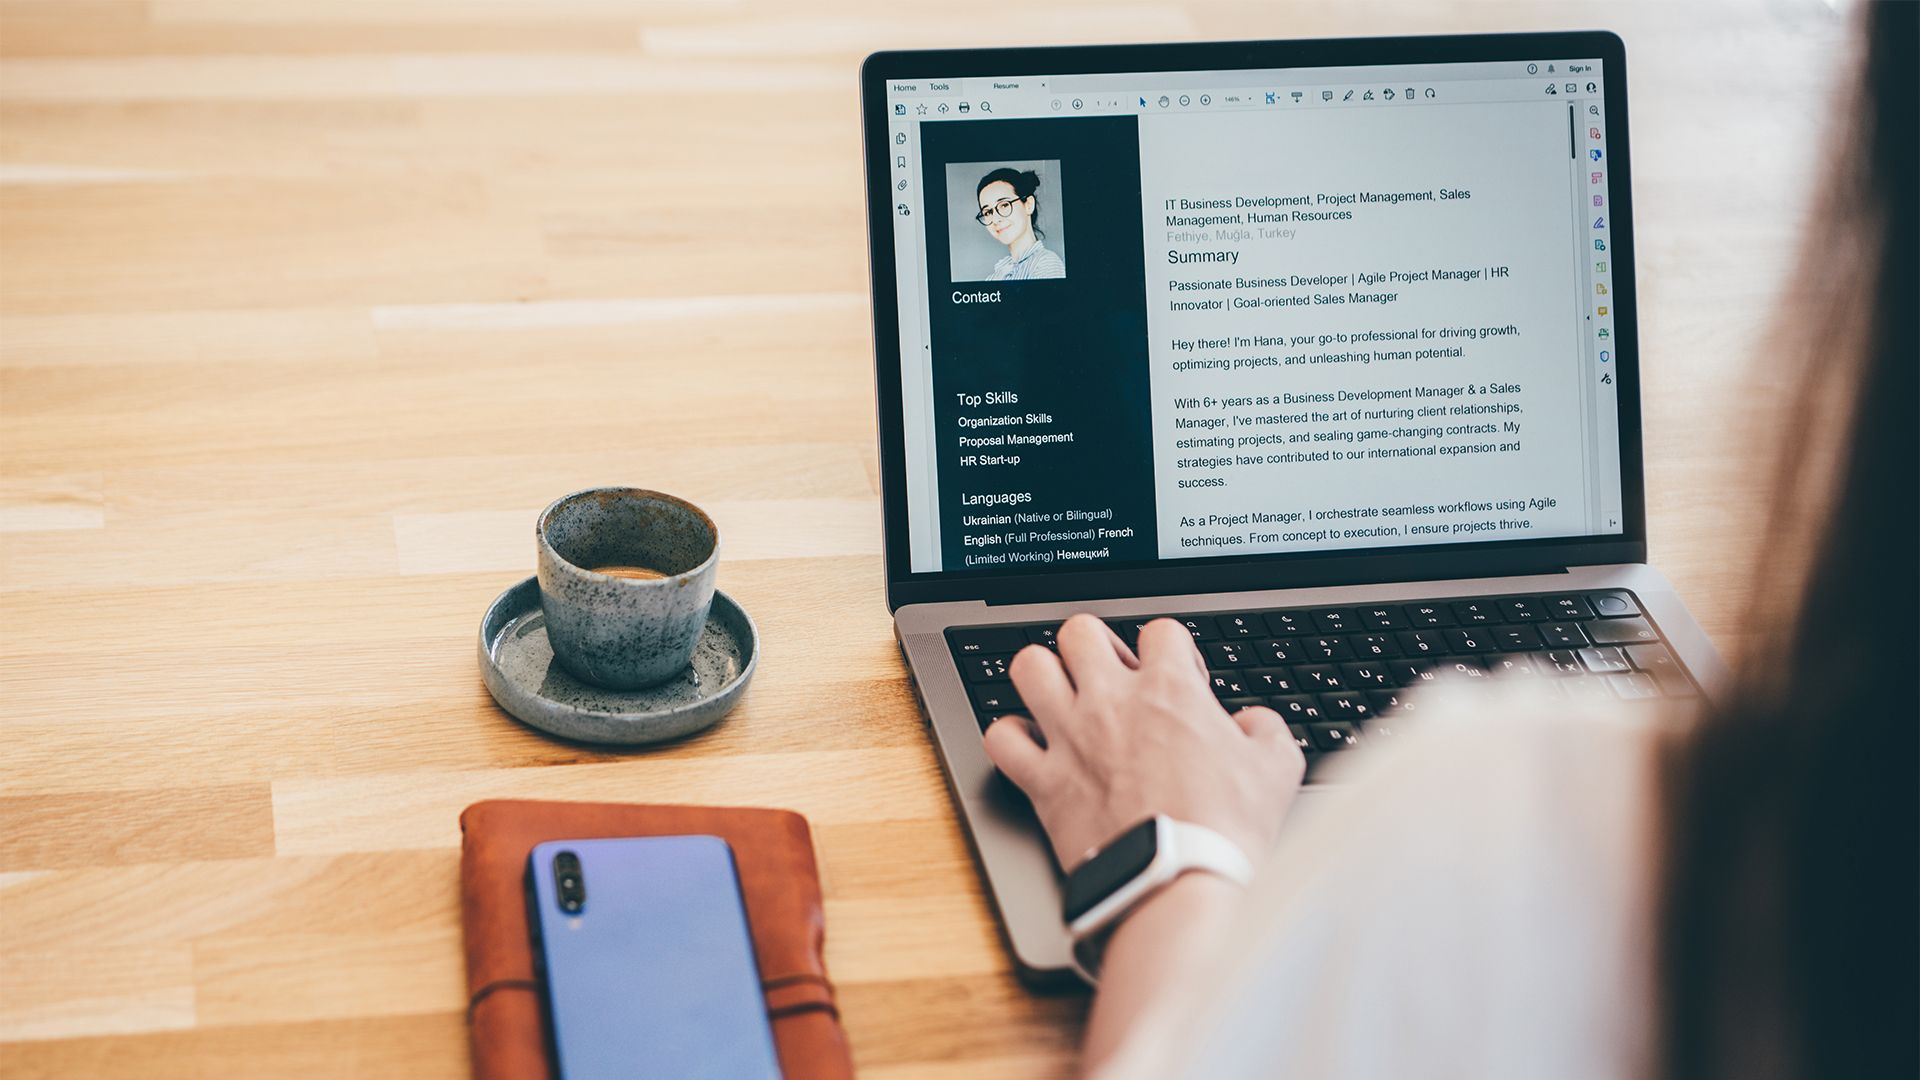
North Korean operatives are increasingly using fake IT worker schemes to infiltrate companies, with reports indicating that they submit up to 60 job applications daily. These operatives create fabricated identities and utilize deepfake technology to appear credible during interviews. Recent incidents include attempts to deploy malware on company devices, with the group known as PurpleDelta creating at least 22 fake personas. Security agencies have issued alerts as these schemes expand beyond North America, affecting organizations globally. The WaterPlum group has reportedly infected over 30,000 devices and stolen approximately $10.7 million from cryptocurrency wallets. The evolving tactics make it challenging for organizations to distinguish between genuine applicants and criminals. Companies are advised to implement stringent hiring practices to mitigate these risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track FAMOUS CHOLLIMA and Huntress in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How can we identify fake candidates?
What sectors are most affected?
What steps should we take to mitigate this threat?
Continue Reading
 US Disrupts North Korean Laptop Farms Generating $3 Million in Fraud The US Department of Justice has arrested two US nationals, Michael James Bostelle and Juan Cecilio Pena Carrillo, for their roles in a scheme that facilitated North Korean IT workers to obtain remote jobs at US companies using stolen identities. This operation, named 'Operation Lonestar Roundup', involved raids on…
 AI Agents Exploit Software Supply Chain Vulnerabilities In March 2026, an attacker backdoored the GitHub Action for Trivy, a popular open-source security scanner, allowing the compromise of LiteLLM's CI/CD pipeline. This incident led to the publication of two malicious releases on PyPI, affecting over 2,000 organizations. OWASP’s GenAI Security Project highlighted prompt…