 www.prnewswire.co.uk
Rockwell Automation Launches CompactLogix 5390 Controller with Enhanced Cybersecurity Features
Article Content

- •Rockwell Automation launched the CompactLogix 5390 controller on October 13, 2026.
- •The controller features built-in cybersecurity aligned with IEC 62443-4-2.
- •It is designed to simplify machine design while addressing regulatory safety and cybersecurity needs.
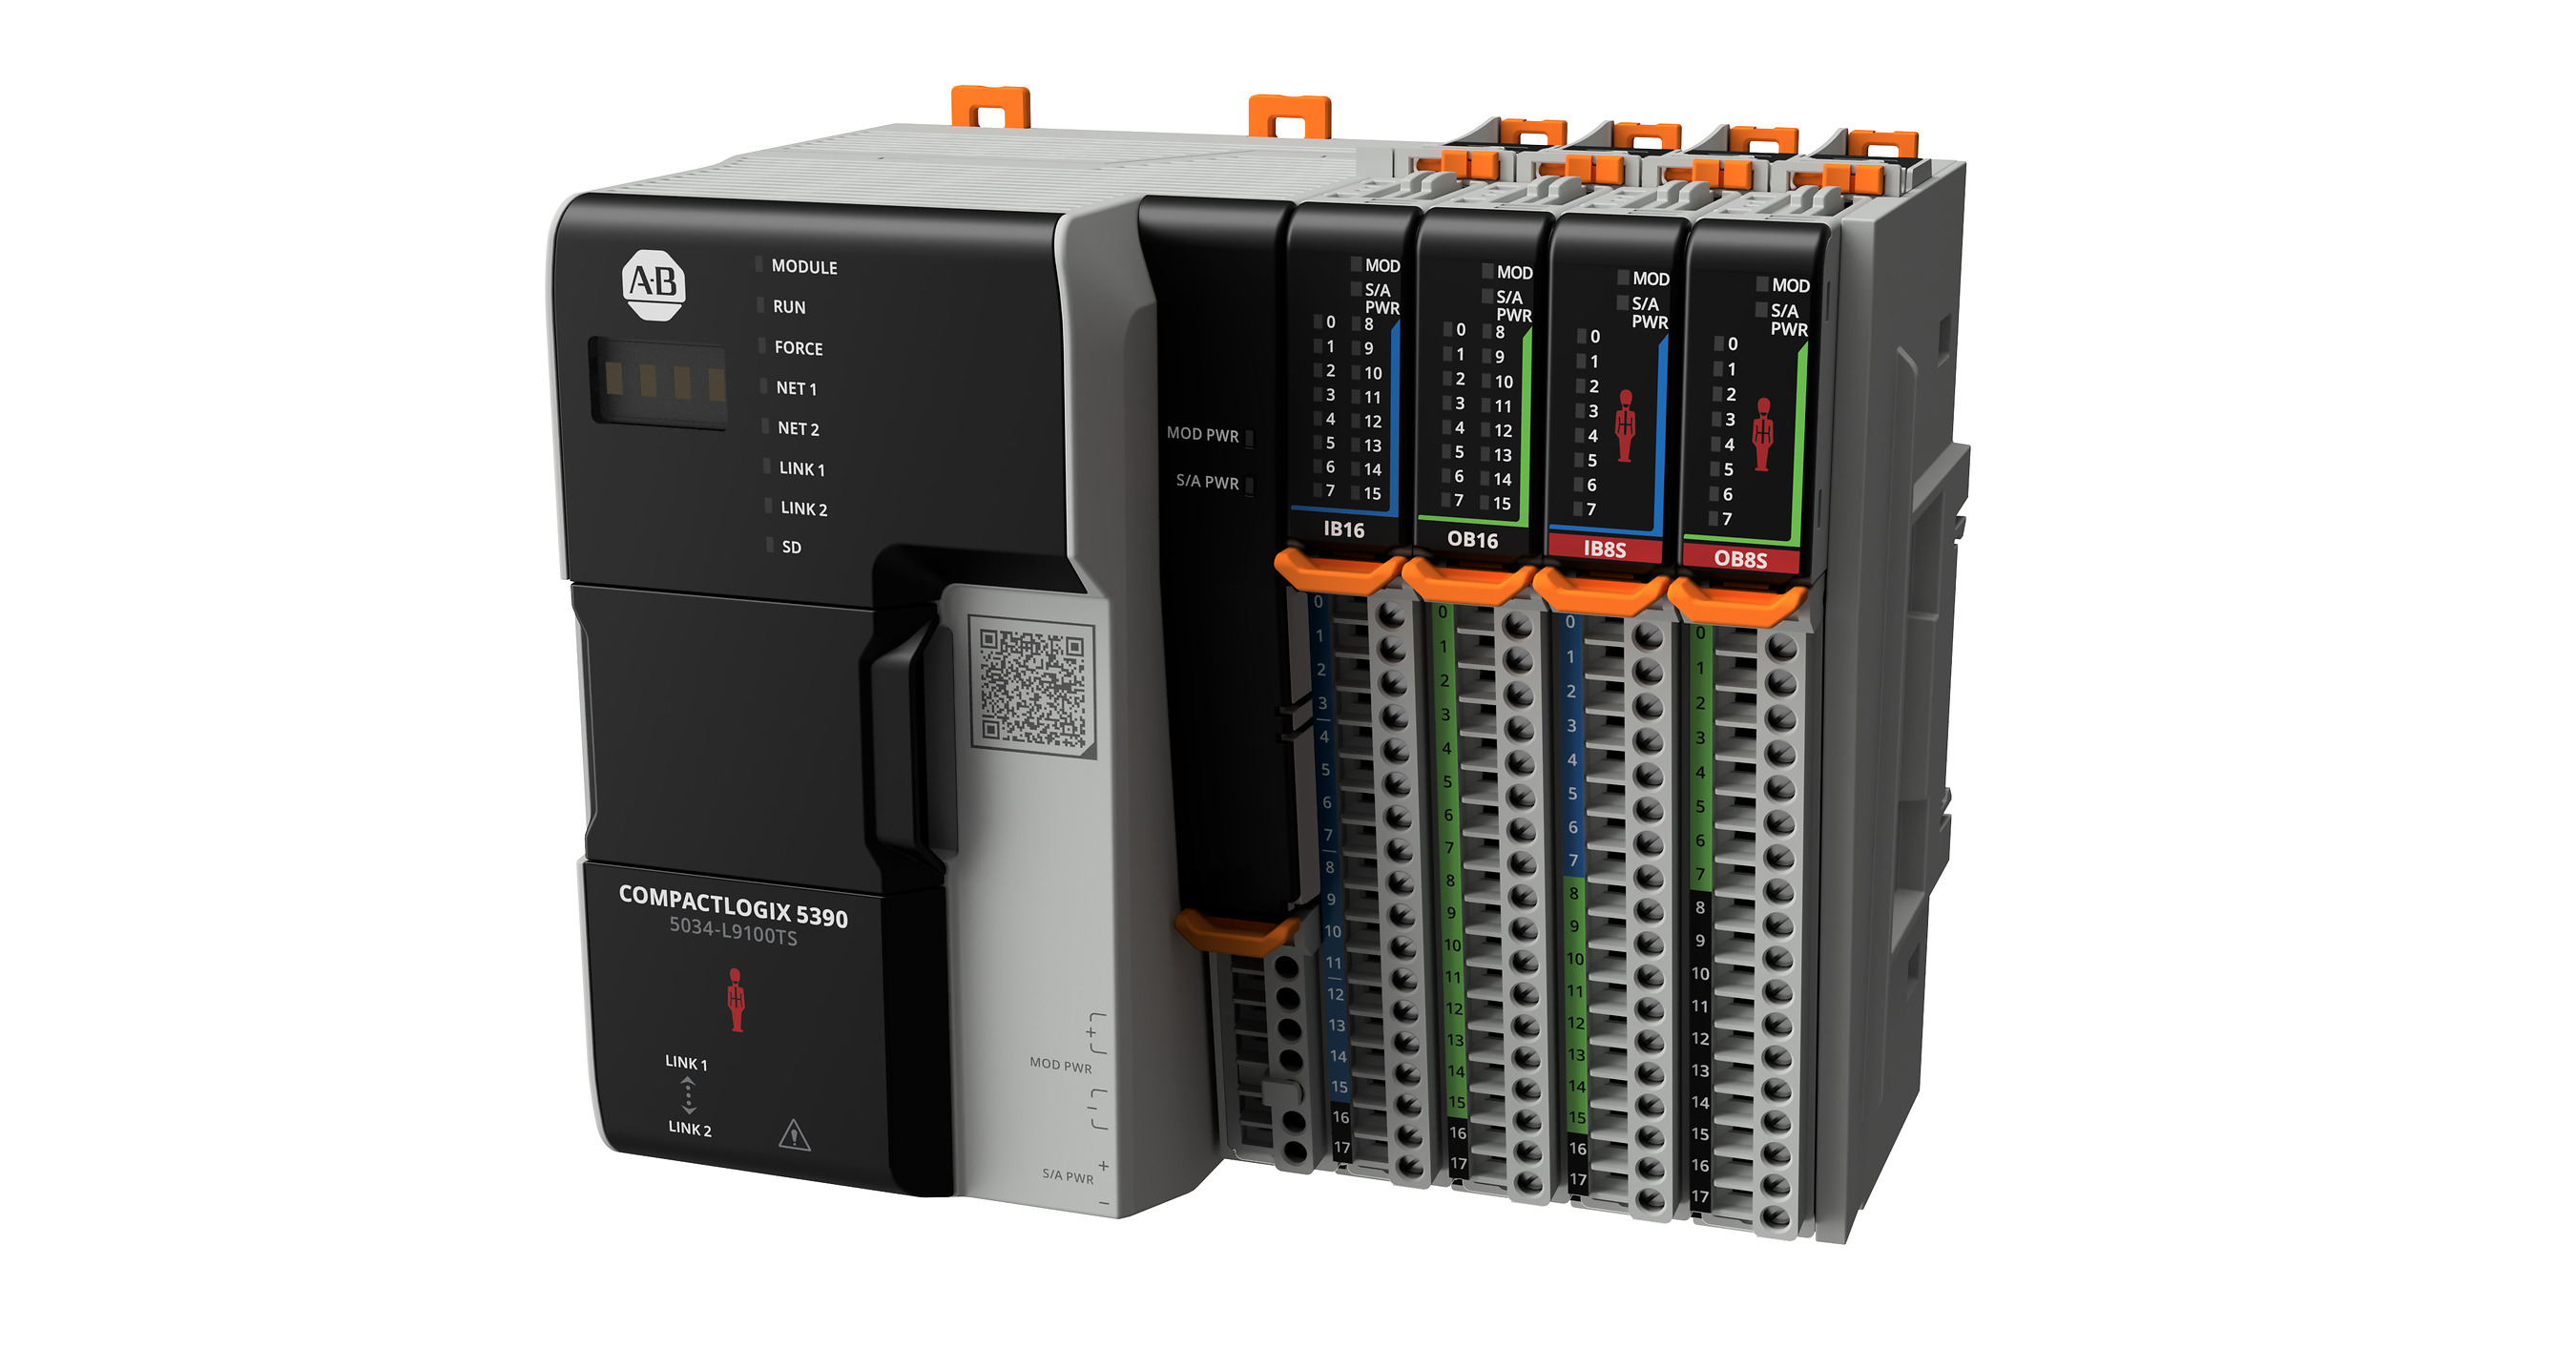
On October 13, 2026, Rockwell Automation announced the launch of the CompactLogix® 5390 controller, which integrates enhanced performance, safety, and cybersecurity capabilities. This controller is designed to help machine builders and manufacturers meet increasing operational and regulatory demands in a connected industrial environment. The CompactLogix 5390 supports built-in cybersecurity aligned with IEC 62443-4-2 and is prepared for the EU Cyber Resilience Act. It also features local PointMax™ I/O support for modular architectures and is 43% smaller than its predecessor, CompactLogix 5380. The introduction of this controller aims to simplify machine design while addressing stringent safety and cybersecurity requirements. Rockwell Automation emphasizes that the new controller will help customers manage complex automation applications with reduced engineering effort.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are the key features of the CompactLogix 5390 controller?
How does this controller address cybersecurity?
What is the significance of the 43% smaller footprint?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…