 Trtworld
Russia Accuses Ukraine of Escalating Attacks on Zaporizhzhia Nuclear Power Plant
Article Content

- •Russia claims Ukraine intensified attacks on the Zaporizhzhia Nuclear Power Plant.
- •Accusations include targeting civilian facilities and creating radiological risks.
- •The IAEA has personnel at the plant, which remains under Russian control.
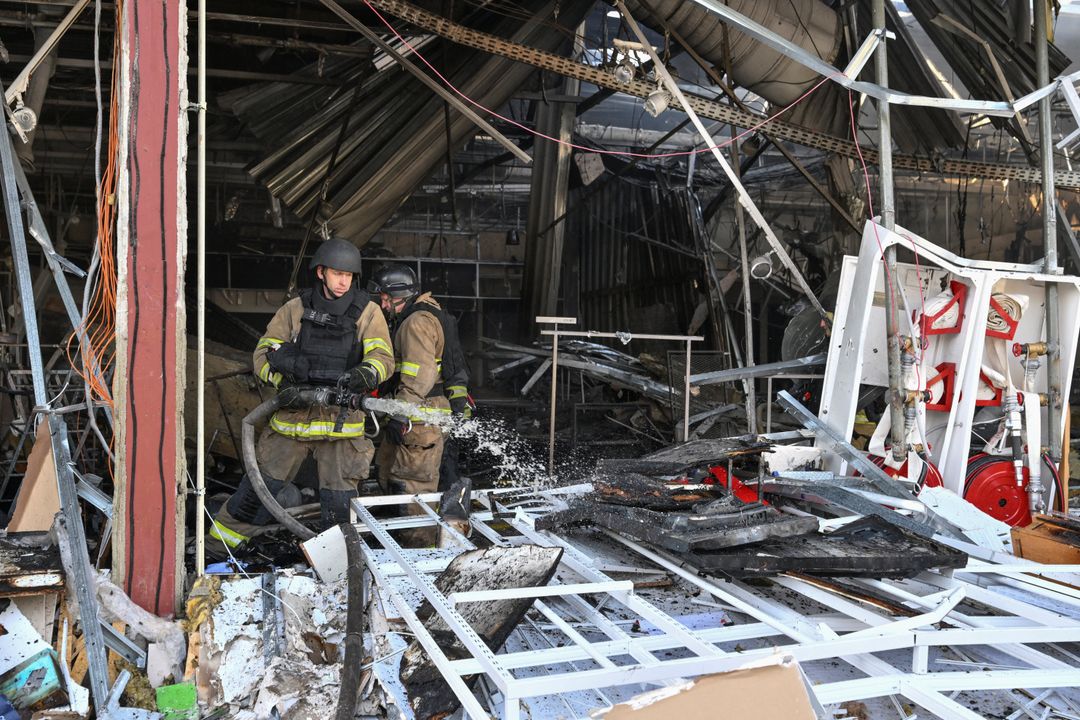
On October 26, 2026, Russia accused Ukraine of intensifying attacks on the Zaporizhzhia Nuclear Power Plant and the nearby city of Enerhodar. Russian Foreign Ministry spokesperson Maria Zakharova criticized the International Atomic Energy Agency (IAEA) for its restrained response to these actions. She claimed Ukrainian forces targeted civilian facilities, including an art school and a fire and rescue station. Zakharova alleged that Ukraine's actions aimed to destabilize the plant's operations and create a radiation-contaminated zone. The situation remains tense, with ongoing concerns about a potential nuclear disaster as both nations accuse each other of attacks around the facility. The IAEA has personnel stationed at the plant since September 1, 2022, and Russia has controlled it since March 2022.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What specific actions did Russia accuse Ukraine of?
What is the current status of the Zaporizhzhia Nuclear Power Plant?
What are the implications of these accusations?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 PHP2Shell Vulnerabilities Exploited by AI-Driven Attackers Threat actors have exploited PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619) to target a government entity in Europe, gaining access to sensitive data within two hours of the initial breach. The attackers utilized AI tools for reconnaissance and post-exploitation activities, including accessing…