 Therecord.Media
Russia Arrests DataSuckers Hackers Linked to Major Breaches
Article Content

- •Three members of the DataSuckers hacking group have been arrested in Russia.
- •The group exploited exposed GitHub credentials to breach systems of major companies.
- •Denis Fridman faces charges related to the Dodo Pizza data breach affecting millions.
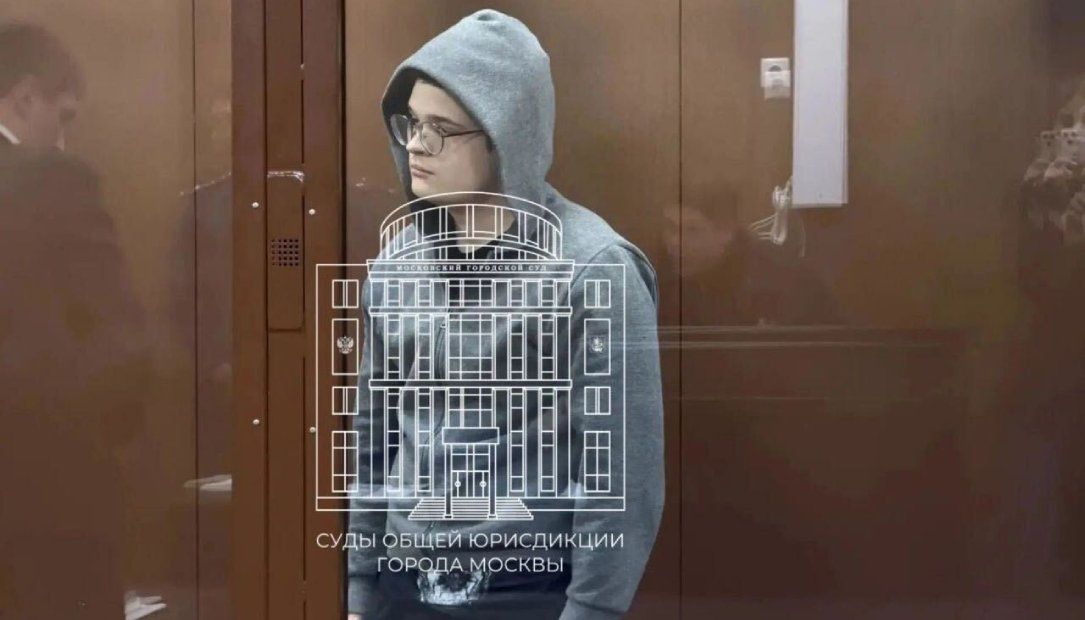
Russian authorities have detained three members of the DataSuckers hacking group, which has been linked to significant cyberattacks on businesses in Russia and Ukraine, including Dodo Pizza, Tez Tour, and ATB Market. The group reportedly exploited exposed corporate credentials found on GitHub to access sensitive systems. The primary suspect, 19-year-old Denis Fridman, was placed under house arrest until December 8 and faces charges related to the illegal handling of personal data. The breach of Dodo Pizza is particularly concerning, as it involved the theft of customer information from over 15 years of orders. The stolen data was reportedly offered for sale on the dark web for $100,000. The group has emerged as a notable threat in the region, with a modus operandi that includes data theft and extortion. Authorities are continuing to investigate the group, which has members across Russia, Belarus, and Kazakhstan.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track ATB in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was compromised in the Dodo Pizza breach?
What charges does Denis Fridman face?
What should businesses do to protect against similar attacks?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…