 Lbc
Russia Issues Arrest Warrant for Former UK Defense Chief Over Kerch Bridge Comments
Article Content

- •Russia has issued an arrest warrant for former UK Defense Secretary Ben Wallace.
- •Wallace's comments at the Warsaw Security Forum advocated for military action against the Kerch Bridge.
- •The Kerch Bridge is a strategic military route for Russia and has been targeted by Ukraine.
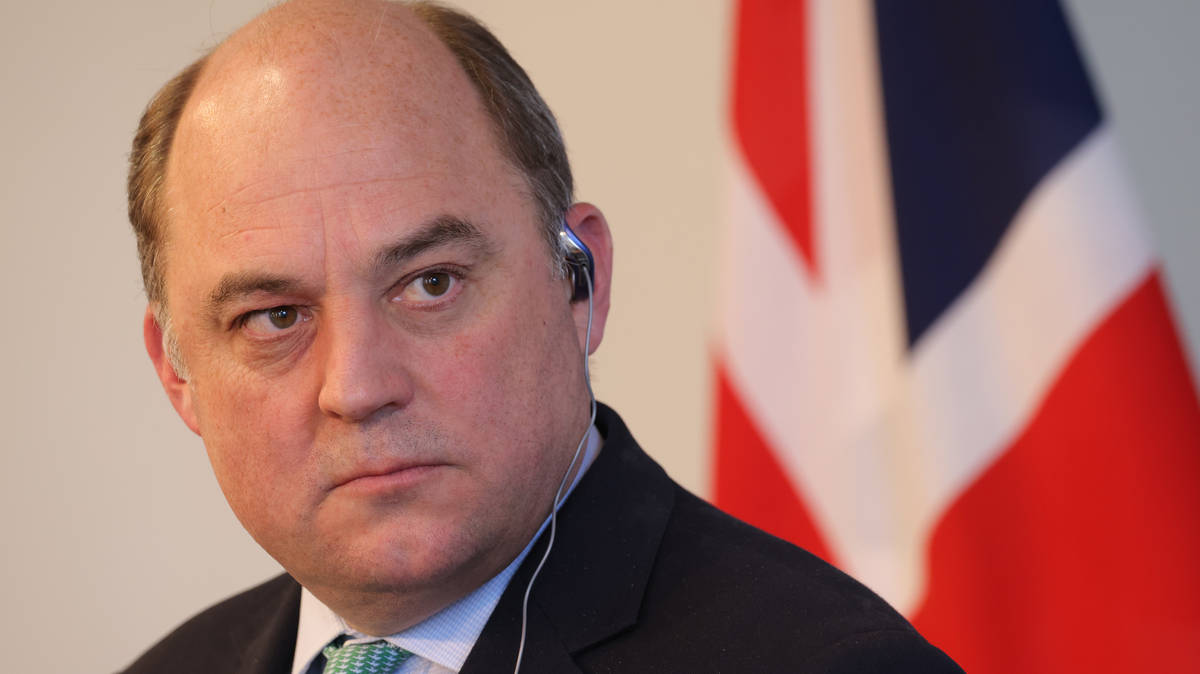
Russia has issued an arrest warrant for former UK Defense Secretary Ben Wallace after he called for Ukraine to target the Kerch Bridge, a critical military logistics route for Russia. The Basmanny District Court sentenced Wallace in absentia for 'justifying terrorism' based on remarks made during the Warsaw Security Forum in September 2025. Wallace's comments included a call to make Crimea 'unviable' for Russian forces and to 'smash the Kerch Bridge.' The Kremlin condemned his statements as incitement to terrorism, and Russian lawmakers had previously pushed for his arrest. Wallace, who served as defense chief from 2019 to 2023, has been a vocal supporter of Ukraine amidst the ongoing conflict. The Kerch Bridge, linking Russia to Crimea, has been a target of multiple Ukrainian attacks since 2022. Wallace's arrest warrant reflects escalating tensions between Russia and Western nations regarding support for Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…