 United24Media
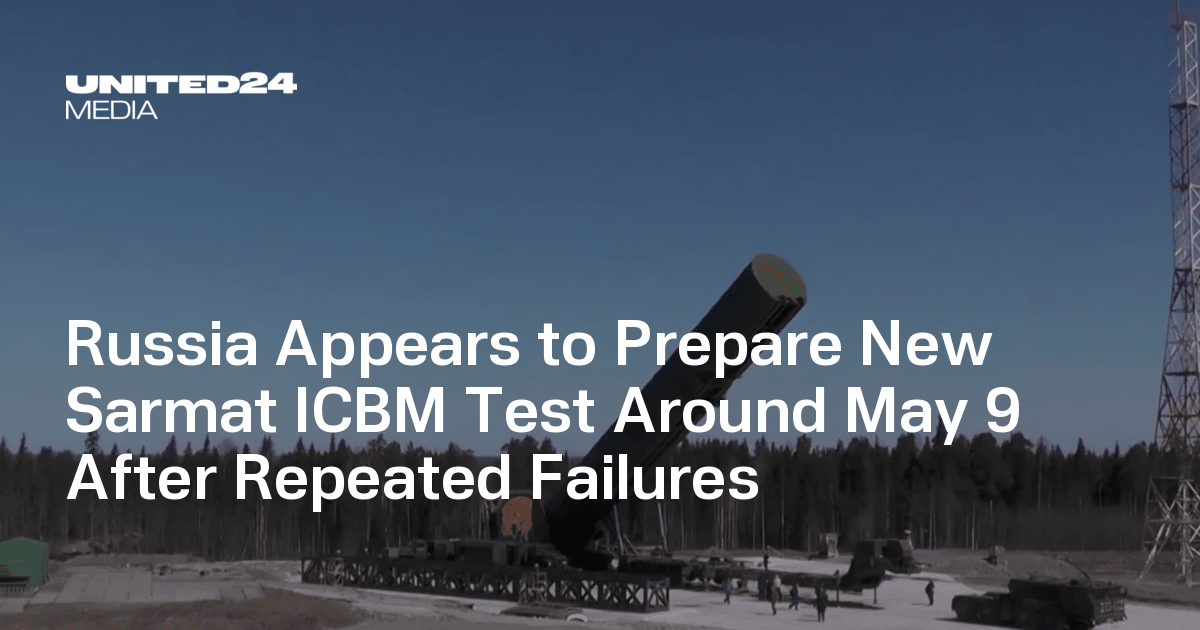
Russia Prepares for Sarmat ICBM Test Amid Ongoing Failures
Article Content

- •Russia is preparing for a Sarmat ICBM test around May 9, a significant date in its military calendar.
- •The Sarmat missile program has faced multiple failures, including a recent test where the missile crashed after launch.
- •Analysts believe the Kremlin is using missile tests to project strength amid security concerns over traditional military displays.
Russia is reportedly preparing for another test of its Sarmat intercontinental ballistic missile (ICBM) around the symbolic May 9 Victory Day. Aviation warnings and missile range closures indicate a potential launch window between May 8 and May 11. Recent tests of the Sarmat missile have faced significant setbacks, including a failed launch in November 2025 where the missile crashed shortly after takeoff. Analysts suggest that the Kremlin may be attempting to project military strength due to the cancellation of traditional military parades over security concerns. The Sarmat missile, intended to replace aging Soviet-era systems, has yet to enter operational service despite over a decade of development. The last successful test occurred in April 2022, marking a troubling trend for Russia's missile program. The ongoing failures raise questions about the reliability of Russia's nuclear deterrent capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (16)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…