 Kyivindependent
Russia Resumes Grain Shipments Amid Ongoing Conflict
Article Content

- •Russia has resumed grain shipments after a three-month halt due to Ukrainian drone strikes.
- •Over 100 Russian vessels were reportedly hit during the summer, impacting grain exports and prices.
- •A localized ceasefire has been established to allow safe passage for humanitarian supplies.
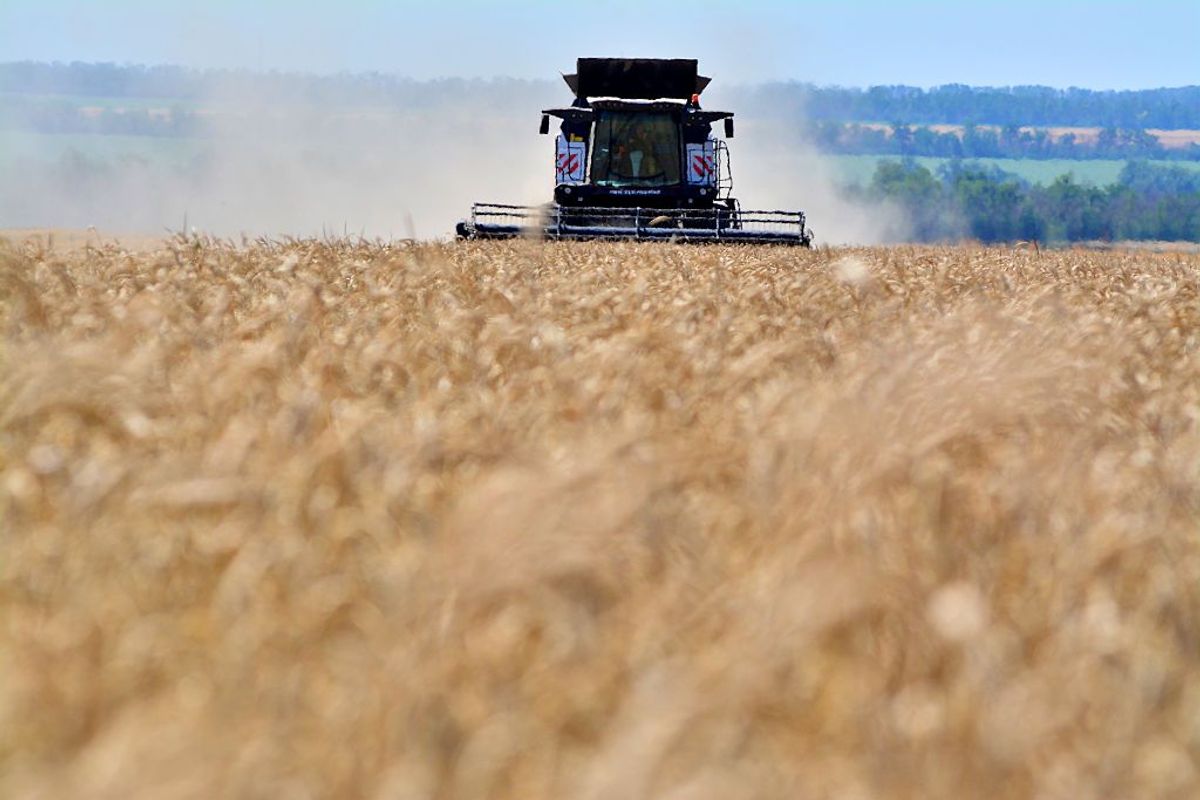
Russian authorities have restarted grain shipments through the Sea of Azov after a three-month halt due to Ukrainian drone attacks that began on July 10. The resumption follows the issuance of permits for vessels to pass through the Kerch Strait, with reports indicating at least one ship has already made the journey to the Black Sea. The Ukrainian military's Operation Molochka targeted Russian vessels, resulting in over 100 ships being hit during the summer, which significantly impacted Russia's economy and global grain prices. The situation is further complicated by a localized ceasefire mediated by U.S. First Lady Melania Trump, aimed at facilitating humanitarian supplies in the region. Despite the resumption of shipments, both Russia and Ukraine have continued to target each other's maritime assets, affecting the agricultural trade in the Black Sea. The current status indicates a cautious optimism regarding safety in the region, as both sides claim the ceasefire is holding.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What caused the halt in grain shipments?
How many vessels were affected by the attacks?
What is the current status of the ceasefire?
Continue Reading
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…