 United24Media
Russia Seeks Exchange of North Korean POWs Amidst Ukraine Conflict
Article Content

- •Russia has only requested the exchange of two North Korean POWs, ignoring other foreign fighters.
- •The captured North Koreans wish to be transferred to South Korea, complicating legal considerations.
- •Ukraine emphasizes compliance with international humanitarian law regarding the treatment of POWs.
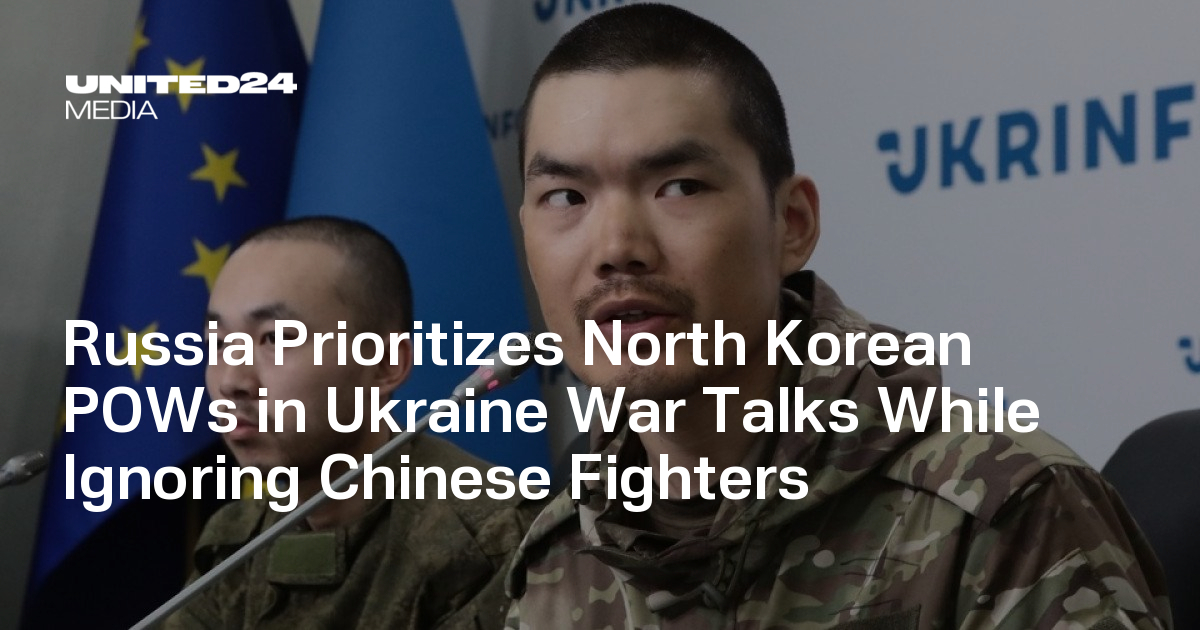
Russia has requested the exchange of two North Korean prisoners of war (POWs) captured by Ukraine, while showing no interest in other foreign fighters detained. Bohdan Okhrimenko, head of Ukraine's POW treatment coordination, stated that the Russians have inquired about the North Koreans multiple times but have not requested any other foreign nationals, including Chinese fighters. The captured North Koreans expressed a desire to move to South Korea, complicating their potential transfer under international humanitarian law. Ukraine remains cautious about the legal implications of the POWs' status and has emphasized adherence to the Geneva Conventions. The situation highlights the ongoing complexities of international law in wartime and the geopolitical dynamics involving North Korea and Russia. As of now, the two North Korean soldiers are receiving medical care in Ukraine.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…