 Theguardian
Russian Artist and Putin Critic Shot Dead in Poland
Article Content

- •Robert Kuzovkov, a Russian artist and critic of Putin, was shot dead in Poland.
- •The attack occurred in a car park, with five shots fired, including one to the head.
- •Two Belarusian citizens have been detained, but their involvement is still unclear.
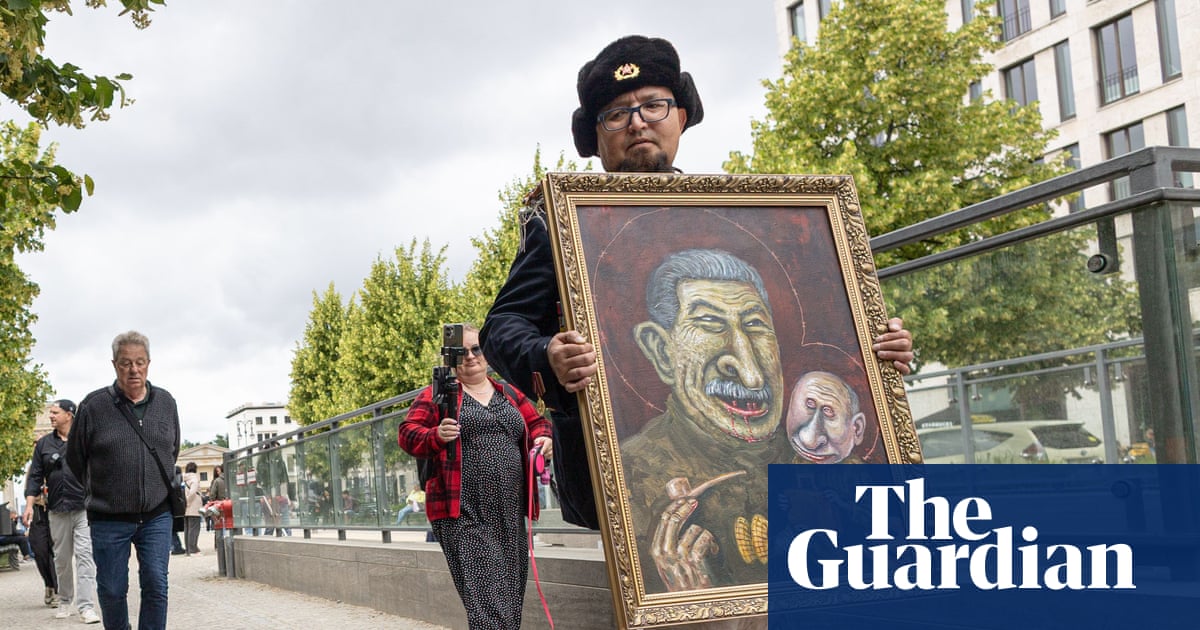
Robert Kuzovkov, a Russian artist known as Semyon Skrepetsky and a vocal critic of Vladimir Putin, was shot dead in Biała Podlaska, Poland, on June 16, 2026. The attack occurred in a car park, where he was shot five times, including in the head. Two Belarusian citizens have been detained in connection with the murder, although their involvement is still under investigation. Kuzovkov had recently participated in a protest in Berlin against Russian authorities, showcasing his artwork that criticized Putin and other leaders. The incident is being treated as a targeted assassination, potentially linked to his outspoken views against the Russian government. Polish authorities are collaborating with the Internal Security Agency to investigate the murder, which has raised concerns about the safety of dissidents in Poland. Local media suggest the killing may bear the hallmarks of an operation ordered by Chechen leader Ramzan Kadyrov. An autopsy is scheduled for June 17, 2026.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (7)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…