 Cbsnews
Russian Drone Factory Director Injured in Car Explosion Amid Rising Attacks
Article Content

- •Vladimir Tkachuk, director of Uraldronzavod, was injured in a car explosion on August 5, 2026.
- •The explosion is part of a series of targeted attacks against Russian drone manufacturers.
- •Russian authorities have not confirmed the perpetrators but have blamed Ukraine for related incidents.
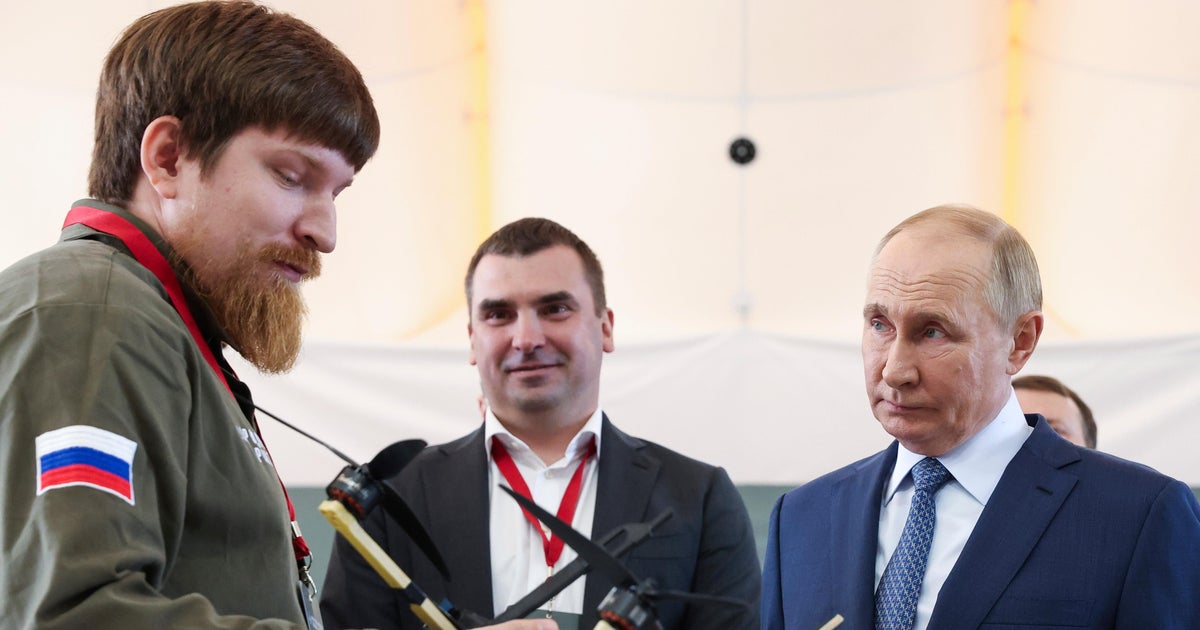
Vladimir Tkachuk, director of Uraldronzavod, was severely injured in a car explosion in Bolshoy Istok, near Yekaterinburg, on August 5, 2026. The explosion, which killed the driver, is believed to be an attempted murder linked to ongoing tensions in the region. Tkachuk's factory produces Upyr drones for the Russian military, and he has previously showcased these drones to President Putin. This incident follows a recent shooting of another drone manufacturer, indicating a pattern of targeted attacks against individuals in the defense sector. The Russian authorities have not confirmed who is responsible for the explosion, but they have blamed Ukraine for various attacks on military officials. The incident occurred one day after a bombing at a Moscow restaurant that killed five people, which Russia also attributed to Ukraine. A criminal investigation into the explosion has been launched, and Tkachuk remains in serious condition in the hospital.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Uraldronzavod in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…