 Greatreporter
Russian Drone Strike in Dnipro Kills 15, Raises Security Concerns
Article Content

- •A Russian drone strike in Dnipro killed 15 people on October 31, 2026.
- •The attack underscores the risks of long-range drones controlled via satellite networks.
- •This incident raises urgent security concerns for European and American civilian safety.
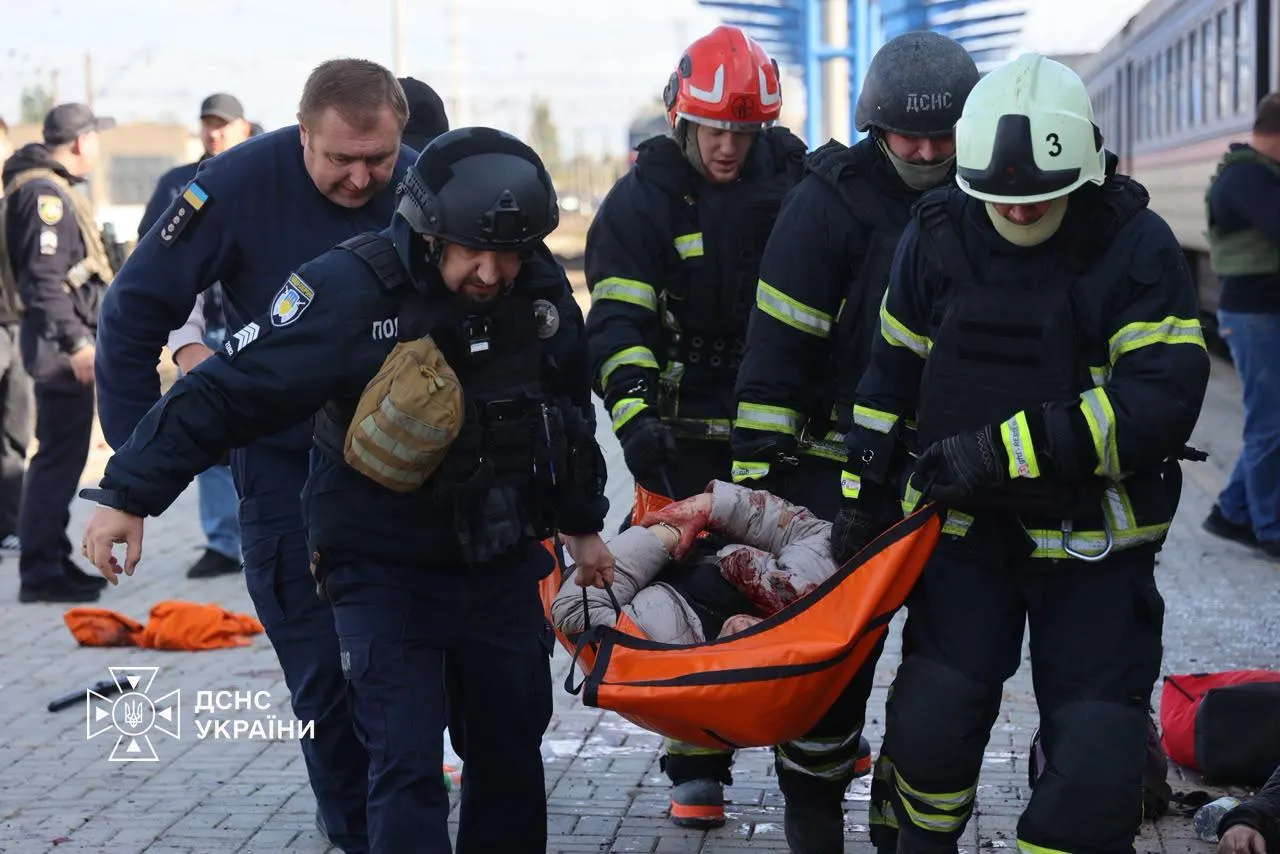
On October 31, 2026, a Russian jet-powered drone struck a crowded railway platform in Dnipro, Ukraine, resulting in 15 fatalities and multiple injuries, including an 11-year-old boy. The attack is part of Russia's ongoing drone campaign against Ukraine, raising alarms about the potential for long-range weapons to operate via independent satellite networks. This incident highlights the risks of drones being controlled remotely from significant distances, potentially allowing operators to target civilian locations with minimal oversight. The aftermath showed severe damage to the railway infrastructure and casualties among civilians. The implications of such attacks extend beyond Ukraine, prompting European and American governments to reconsider their security measures against drone warfare.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What were the casualties from the drone strike?
How does this attack affect European security?
What type of drone was used in the attack?
Continue Reading
 North Korean Hackers Steal $6.3 Billion from Binance in Record Crypto Heist On October 29, 2026, Binance, the world's largest cryptocurrency exchange, reported a massive security breach resulting in the theft of approximately $6.3 billion across ten blockchains. The attack is attributed to North Korea's TraderTraitor hacking group, which gained access via a compromised DevOps engineer's…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…