 Pravda.Ua
Russian Forces Attack Critical Infrastructure in Oleksandriia
Article Content
Browse articles 
- •Russian forces attacked critical infrastructure in Oleksandriia on October 7.
- •The attack resulted in one death and three injuries, with ongoing rescue operations.
- •Local authorities are still confirming details and assessing the full impact of the attack.
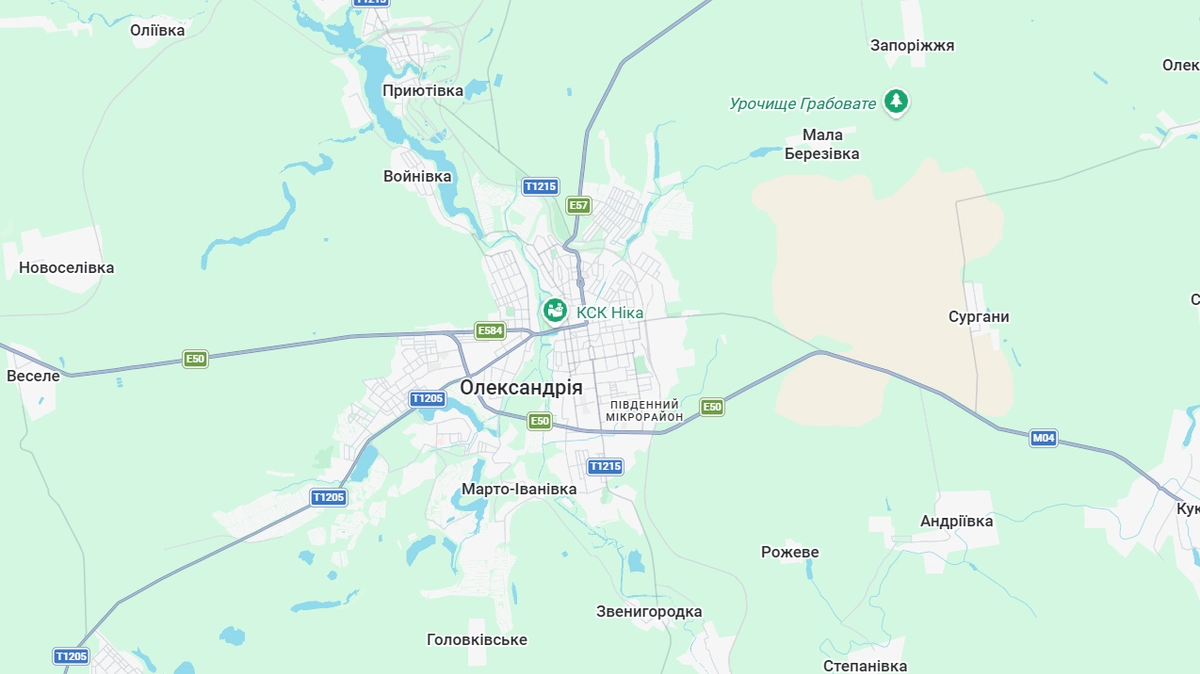
On October 7, 2026, Russian forces launched an attack on critical infrastructure in Oleksandriia, Kirovohrad region, resulting in one fatality and three injuries. The head of the Oleksandriia community, Serhii Kuzmenko, confirmed the attack involved multiple strikes on infrastructure facilities. Emergency medical teams were dispatched to assist the injured. Rescue units are working on the aftermath, and further details are being confirmed. The attack is part of ongoing military actions in the region, with local authorities reporting on the situation through social media. The full scope of the damage and additional casualties is still being assessed.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
2026-10-07
Russian forces attack critical infrastructure
Multiple strikes on infrastructure in Oleksandriia led to one death and three injuries, with emergency services deployed.
Ukrinform2026-10-07
Emergency response initiated
Emergency medical teams and rescue units were dispatched to assist the injured and manage the aftermath of the attack.
Pravda.UaMore articles in this cluster (2)
Common questions
What infrastructure was targeted?
The attack targeted critical infrastructure facilities in Oleksandriia, although specific systems affected have not been detailed.
How many people were injured?
The attack resulted in three reported injuries and one confirmed fatality.
What is the current status of the emergency response?
Emergency medical teams and rescue units are actively responding to the situation and assessing the damage.
Continue Reading
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…