Article Content

- •A laboratory worker in Siberia died from severe pneumonia, raising fears of pneumonic plague.
- •Russian authorities quarantined 200 contacts, but no secondary cases have been confirmed.
- •Experts emphasize the need for transparency from Russian health officials regarding the incident.
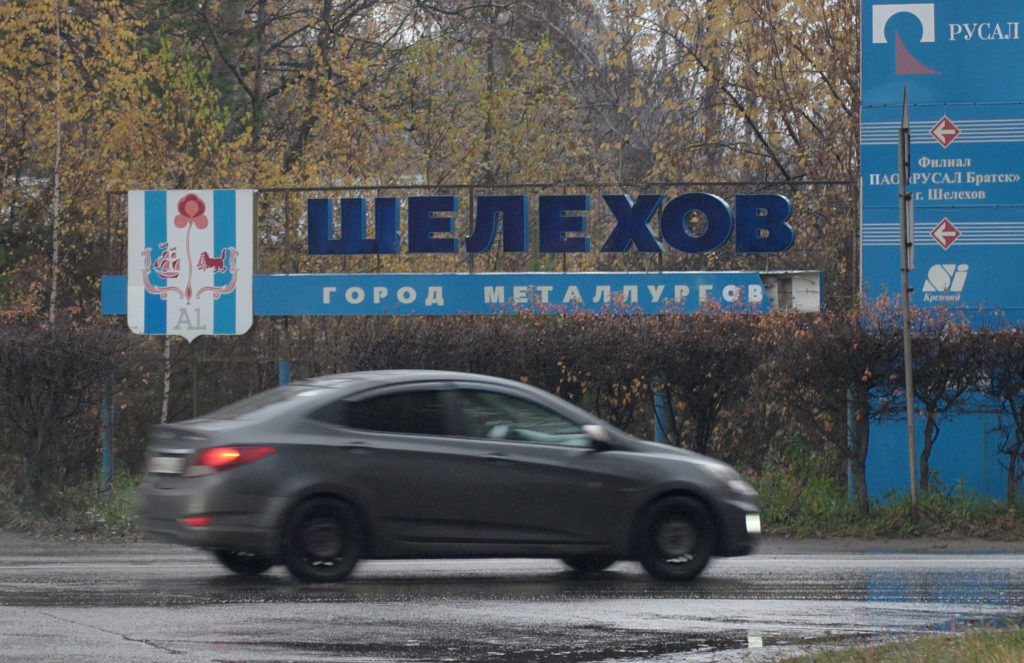
Darya Shipilova, a 28-year-old laboratory worker at an anti-plague institute in Siberia, died on October 2, 2026, reportedly from severe pneumonia. Initial reports suggested a possible pneumonic plague infection, prompting the World Health Organization (WHO) to investigate. Russian authorities quarantined 200 contacts and isolated a hospital, indicating a serious response despite claiming no recent plague cases in the region. Experts believe the situation does not currently indicate a pandemic risk, but they express concern over the lack of transparency from Russian officials regarding the pathogen involved. The WHO has requested further information on the tests conducted and the circumstances surrounding Shipilova's illness. As of now, no secondary cases have been confirmed, and the health risk is assessed as low. The incident has revived public distrust towards Russian health authorities, reminiscent of the early COVID-19 response.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What pathogen caused the lab worker's illness?
What actions were taken by Russian authorities?
What is the current health risk assessment?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…