 en.defence-ua.com
Russia's Black Sea Drone Campaign Disrupted by Starlink Shutdown
Article Content

- •Russia's USV operations in the Black Sea were disrupted by the Starlink shutdown.
- •Attempts to replace Starlink communications with alternative systems have failed.
- •Ukraine has successfully targeted Russian naval assets using USVs since 2022.
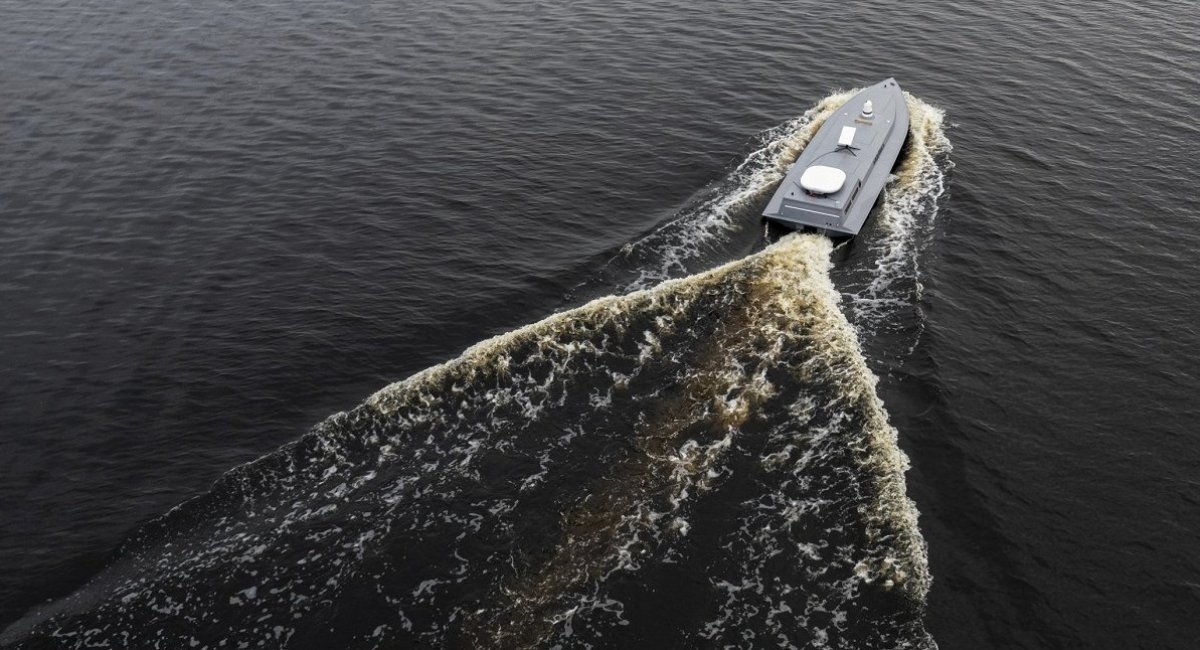
In early 2026, Russia's plans to expand its unmanned surface vehicle (USV) operations in the Black Sea were thwarted after access to Starlink satellite communications was blocked at Ukraine's request. Serhii 'Flash' Beskrestnov, an advisor to Ukraine's Ministry of Defense, reported that Russian forces had been preparing for a broader USV campaign, having developed operational prototypes by mid-2025. Following the Starlink shutdown, Russian attempts to implement alternative communication systems for their USVs failed, leading to significant operational disruptions. The loss of secure communication channels has severely impacted Russian coordination and efficiency in naval operations. Despite these setbacks, Beskrestnov cautioned against underestimating Russia's resolve to deploy USVs, as they have already built several units. Ukraine has effectively utilized USVs since 2022, targeting Russian naval assets and infrastructure. The situation remains dynamic as Russia continues to seek solutions to restore its maritime drone capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…