 Independent
Russia's Covert Drone Shipments to Iran Amid Ongoing Conflict
Article Content

- •Russia is completing covert shipments of drones and supplies to Iran amid ongoing conflict.
- •Ukraine claims to have evidence of Russia providing military intelligence to Iran.
- •Kremlin denies allegations of lethal support, calling them false.
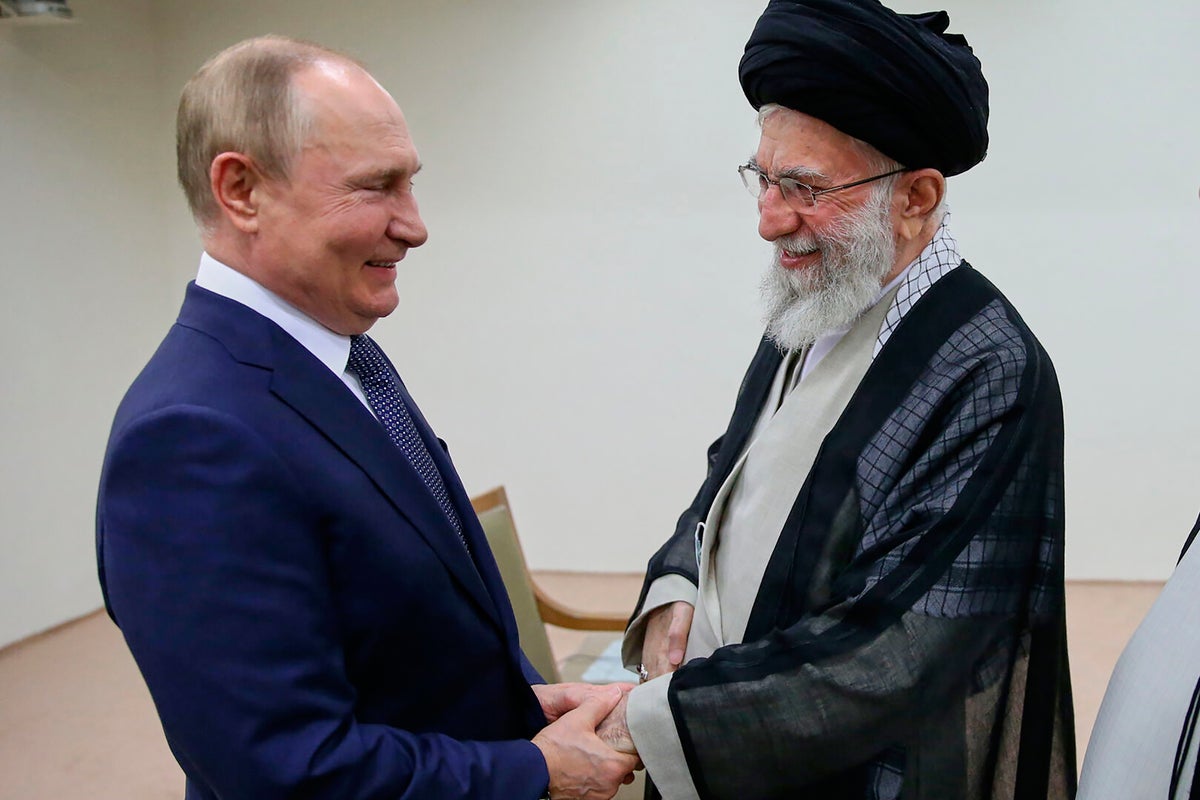
Russia is reportedly completing phased shipments of drones, medicine, and food to Iran, aimed at bolstering Tehran's war efforts against the US and Israel. These covert deliveries began in early March 2026 and are expected to conclude by the end of the month, following discussions initiated shortly after US-Israeli strikes on Iran. The shipments mark a significant shift, as they could represent Moscow's first provision of lethal support to Iran since the onset of the conflict. Concurrently, Ukraine claims to have 'irrefutable' evidence that Russia is providing military intelligence to Iran, which could enhance Iran's targeting capabilities against American forces. The Kremlin has dismissed these allegations as false, emphasizing ongoing dialogue with Iranian leadership. The situation indicates deepening military ties between Russia and Iran, raising concerns about the implications for regional stability and security. Western intelligence suggests that the drones may include advanced capabilities that could significantly enhance Iran's military operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…