 Unn.Ua
Russia's Disinformation Campaign: Fake Memorials Planned at Ukrainian Embassies
Article Content

- •Russia is staging fake memorials at Ukrainian embassies to spread disinformation.
- •The campaign distorts the events of May 2, 2014, in Odesa, portraying Ukraine negatively.
- •Experts emphasize the need for vigilance against manipulative narratives and propaganda.
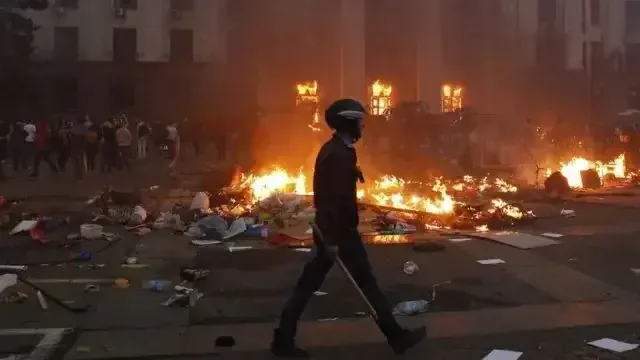
On May 2, 2026, the Center for Countering Disinformation reported that Russia is orchestrating a disinformation campaign by staging fake memorials at Ukrainian embassies worldwide, aimed at discrediting Ukraine. These events, disguised as tributes to the victims of the May 2 tragedy in Odesa, involve organized protests with flower-laying, pro-Russian slogans, and fabricated testimonies for local media. This annual propaganda effort revives the narrative of 'Ukrainian Nazis' committing atrocities, distorting the real events where pro-Russian militants attacked a peaceful march, leading to a tragic fire. The campaign is reportedly intensifying this year, with a focus on influencing international public opinion and destabilizing perceptions of Ukraine. Experts warn that these actions are part of a broader information warfare strategy. The impact is global, affecting Ukrainian diplomatic missions and international relations. Verification of sources and narratives is crucial to counter this manipulation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…